Skip to content
pog0 OffSec
  • Home
  • ToolsExpand
    • My IP: Check Your Public IP (IPv4 & IPv6)
    • Browser Fingerprint: Test and Practical Explanation
    • Secure Password Generator
  • eBooks
  • CheckoutExpand
    • Transaction Failed
    • Confirmation
    • Order History
    • Receipt
  • Links
  • Contact
  • About
pog0 OffSec
  • FeaturedAI Security

    Advanced Threat Modeling: Identities, Trust Boundaries, and Attack Chains

    Advanced threat modeling in practice: identities, trust boundaries, SSRF, cloud metadata, delegated tokens, and blast radius across real attack chains.

    June 17, 202613 min read
    Read article
    Featured image about advanced threat modeling with trust boundaries, identities, and attack chains in an offensive security context.
  • Abstract operational timeline showing a narrow intervention window before ransomware encryption.
    Defensive Security

    Gunra Before Encryption: Detect the Ransomware Handoff

    Bypog0 August 13, 2026August 12, 2026

    Gunra’s locker is the last stage. Detect the earlier handoff from VPN compromise to remote access, exfiltration, backup deletion, and offline encryption.

    Read More Gunra Before Encryption: Detect the Ransomware HandoffContinue

  • Architectural cutaway of a browser-fingerprinting gate routing most sessions to a benign decoy while one selected macOS session reaches a concealed Terminal path.
    Defensive Security

    The Page Was Blank: Inside macOS ClickFix Cloaking

    Bypog0 August 11, 2026August 7, 2026

    A macOS ClickFix campaign hid its lure behind browser fingerprinting. This analysis reproduces the gate safely and builds detection across web, endpoint and identity telemetry.
    Read More The Page Was Blank: Inside macOS ClickFix CloakingContinue

  • Top-down forensic software-release dossier with component cards, dependency threads, artifact evidence and a precise VEX decision marker.
    Software Supply Chain Security

    An SBOM Is Not an Alarm: Build a VEX Decision Pipeline

    Bypog0 August 6, 2026August 5, 2026

    CISA’s 2026 SBOM baseline improves software identity and evidence quality. This advanced guide turns that inventory into an auditable VEX pipeline for exploitability decisions, release policy, and detection.
    Read More An SBOM Is Not an Alarm: Build a VEX Decision PipelineContinue

  • Editorial cutaway of a CI/CD build server exposing an agent polling path through a broken trust boundary into artifact and deployment systems.
    News & Analysis

    CVE-2026-63077: When TeamCity Deserializes Trust

    Bypog0 August 4, 2026August 3, 2026

    CVE-2026-63077 exposes every TeamCity On-Premises version to unauthenticated RCE through the agent polling protocol. This deep dive maps the trust failure, runs a safe deserialization mechanism lab, and shows how to detect, contain, and validate CI/CD integrity.
    Read More CVE-2026-63077: When TeamCity Deserializes TrustContinue

  • Forensic editorial scene showing a benign email feeding a crimson execution path into browser storage, mailbox folders, and network telemetry.
    Defensive Security

    OWAReaper and the Half-Click: When Reading Email Runs Code

    Bypog0 July 30, 2026July 29, 2026

    TA488 turned ordinary webmail rendering into browser-resident access. Trace OWAReaper from reading pane to persistence, then hunt its mailbox and browser artifacts.
    Read More OWAReaper and the Half-Click: When Reading Email Runs CodeContinue

  • Abstract cutaway showing a red path bypassing a metal security patch to reach protected filesystem layers
    Defensive Security

    CVE-2025-68686: The FortiOS Patch Bypass That Starts After Compromise

    Bypog0 July 29, 2026July 29, 2026

    CVE-2025-68686 is not initial access. It is a FortiOS SSL-VPN symlink patch bypass that turns prior filesystem compromise into remote data exposure.
    Read More CVE-2025-68686: The FortiOS Patch Bypass That Starts After CompromiseContinue

  • Architectural cutaway showing a public issue entering an agentic CI chamber, crossing into a private repository archive, and leaving through a public comment channel.
    AI Security

    GitLost: When a Public Issue Can Read a Private Repo

    Bypog0 July 28, 2026July 28, 2026

    GitLost turned a public GitHub issue into a private-repository disclosure. Trace the confused-deputy chain, reproduce it safely, and harden agentic CI.
    Read More GitLost: When a Public Issue Can Read a Private RepoContinue

  • Top-down forensic evidence board showing WordPress batch requests and route cards shifted out of alignment, with a red path leading through SQL to a patched server package.
    Defensive Security

    wp2shell: How WordPress Route Confusion Became RCE

    Bypog0 July 23, 2026July 22, 2026

    wp2shell chains WordPress REST route confusion with SQL injection to reach pre-auth RCE. Learn the mechanics, affected versions, evidence sources, and safe response workflow.
    Read More wp2shell: How WordPress Route Confusion Became RCEContinue

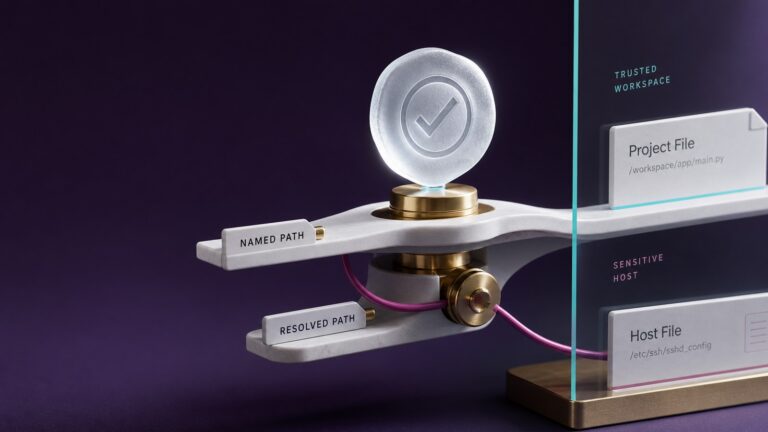
  • Editorial mechanism showing an approved named path secretly resolving through a symbolic link to a sensitive host file outside the trusted workspace.
    AI Security

    GhostApproval: When AI Agent Approval Dialogs Lie

    Bypog0 July 21, 2026July 20, 2026

    GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.
    Read More GhostApproval: When AI Agent Approval Dialogs LieContinue

  • Abstract shared-hosting server divided into many tenant cells with a red compromise path reaching multiple websites
    Defensive Security | News & Analysis

    The Same PHP Web Shell Appeared Across 47 Domains—Here’s How to Hunt It

    Bypog0 July 20, 2026

    A real PHP web shell appeared across 47 domains on one shared host. Hunt its signatures, triage WordPress, preserve evidence, and recover safely.
    Read More The Same PHP Web Shell Appeared Across 47 Domains—Here’s How to Hunt ItContinue

  • Architectural cutaway of an on-premises SharePoint farm showing a red intrusion path crossing web tiers toward server trust material.
    Defensive Security

    SharePoint Exploitation in 2026: Patch, Hunt, and Harden

    Bypog0 July 16, 2026July 15, 2026

    Active SharePoint exploitation demands more than patching. Validate every farm node, hunt IIS and EDR telemetry, rotate trust material, and harden the complete attack path.
    Read More SharePoint Exploitation in 2026: Patch, Hunt, and HardenContinue

  • Featured illustration of an orbital reconnaissance radar mapping exposed internet services for a Shodan.io article.
    Offensive Security

    Shodan.io for Offensive Security: Getting the Most Out of the Internet’s Search Engine

    Bypog0 July 13, 2026July 13, 2026

    Practical Shodan.io guide for security teams: build precise queries, use facets, avoid false positives, automate checks, and validate internet exposure.
    Read More Shodan.io for Offensive Security: Getting the Most Out of the Internet’s Search EngineContinue

  • Forensic incident response desk with encrypted file evidence, verified decryption keys, and a cautious recovery path.
    Ransomware

    Ransomware Recovery: Where to Find Public Decryptors Before You Pay

    Bypog0 July 9, 2026July 8, 2026

    A practical guide for security teams on when public ransomware decryptors work, where to find them, and how to avoid making recovery worse.
    Read More Ransomware Recovery: Where to Find Public Decryptors Before You PayContinue

  • Editorial lab illustration of Frida-style runtime instrumentation probes attached to a translucent Android process with hooks, traces, and red dead-end markers.
    News & Analysis

    Frida for Modern Android Assessments: What Still Works, What Breaks, and Where It Wastes Time

    Bypog0 July 8, 2026July 8, 2026

    Frida remains valuable in Android assessments, but it is most useful when used to validate runtime hypotheses instead of blindly bypassing every control in the app.
    Read More Frida for Modern Android Assessments: What Still Works, What Breaks, and Where It Wastes TimeContinue

  • Forensic editorial illustration of a cracked Android WebView panel, exposed JavaScript-to-native bridge, origin cards, and red security annotations.
    News & Analysis

    WebView Is Still a Mess: Android Hybrid Apps Keep Repeating the Same Security Mistakes

    Bypog0 July 5, 2026July 4, 2026

    WebView remains one of the most productive Android AppSec targets because hybrid apps repeatedly mix trusted native capabilities with untrusted or weakly controlled web content.
    Read More WebView Is Still a Mess: Android Hybrid Apps Keep Repeating the Same Security MistakesContinue

Page navigation

Previous PagePrevious 1 2 3 4 Next PageNext

pog0 OffSec

Practical offensive cybersecurity content: pentest, hardening, AI applied to security, VPN, Linux, and tools for Blue Team and Red Team.

About the Author · Contact

Quick Navigation

  • Home
  • Tools
  • Useful Links
  • Support the Project

Tools and Policies

  • My IP
  • Browser Fingerprint
  • Privacy Policy
  • Affiliate Disclosure

© 2026 pog0 OffSec. Technical content for ethical and authorized use.

LinkedIn
LinkedIn
Share
WhatsApp
X (Twitter)
Post on X
Facebook
fb-share-icon

We use cookies to improve your experience on our site. By continuing to browse this site, you agree to the use of cookies.

Privacy Policy
  • Home
  • Tools
    • My IP: Check Your Public IP (IPv4 & IPv6)
    • Browser Fingerprint: Test and Practical Explanation
    • Secure Password Generator
  • eBooks
  • Checkout
    • Transaction Failed
    • Confirmation
    • Order History
    • Receipt
  • Links
  • Contact
  • About