The Proxy Saw One Request: http4s Ember HTTP Desync
Three http4s Ember flaws let proxies and origins disagree about HTTP request boundaries. Trace the mechanics, safe lab, detection, and durable fixes.

Practical offensive security tradecraft, pentesting, OSINT, exploitation, bug bounty, and adversary emulation.
Three http4s Ember flaws let proxies and origins disagree about HTTP request boundaries. Trace the mechanics, safe lab, detection, and durable fixes.
Jenkins configuration forms can become constructor dispatch. Trace the September 2026 flaws, a safe mechanism lab, detection signals, and durable fixes.
CVE-2026-47849 let JSON Patch mutate Spring Data REST identifiers and version fields. This analysis verifies the binding flaw, traces the cross-record overwrite path, and maps practical detection and hardening controls.
ShieldBreak (CVE-2026-69414) abuses file-path resolution around Microsoft Defender. Trace the privilege chain, detection telemetry, and interim controls.
Unit 42’s Pass-ta-key research exposes device-trust and recovery attacks around Google-synced passkeys. Trace the mechanics, detection, and defensive choices.
Practical Shodan.io guide for security teams: build precise queries, use facets, avoid false positives, automate checks, and validate internet exposure.
How to use ethical hacking labs to train enumeration, exploitation, evidence gathering, and reporting discipline without falling into CTF habits.
The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
An advanced guide to defensive corporate OSINT from a Red Team perspective, covering identity, cloud, APIs, detection, and real attack chains.
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
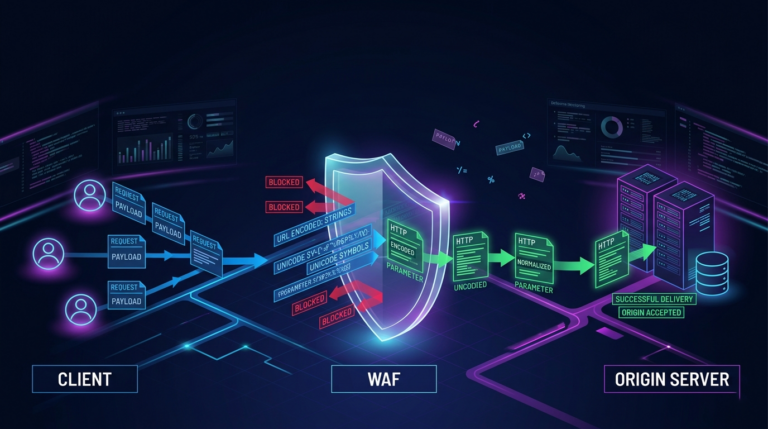
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
A practical lab-based methodology for assessing router security with Claude, MCP, controlled recon, vendor disclosure, and defensible evidence handling.
Why running Nmap on Android changes internal recon: faster enumeration from a mobile foothold, realistic constraints, and practical offensive tradecraft.







