The Template Passed Review: Nuclei Scanner Trust
Five Nuclei flaws show how alternate loaders, embedded runtimes, and response evaluation can turn a security scanner into the asset under attack.

Hands-on tools, utilities, and lab-focused resources for offensive and defensive security practitioners.
Five Nuclei flaws show how alternate loaders, embedded runtimes, and response evaluation can turn a security scanner into the asset under attack.
How to use ethical hacking labs to train enumeration, exploitation, evidence gathering, and reporting discipline without falling into CTF habits.
The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
A practical guide to creating strong passwords with solid cryptography practices and post-quantum readiness. Includes an interactive password generator at the end.
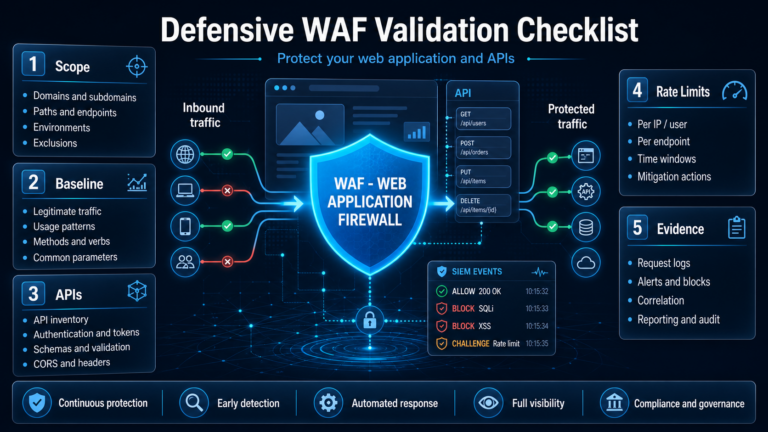
A practical checklist for validating WAF coverage safely: scope, evidence, detection, mitigation, rate limits, false positives, and defensive reporting.
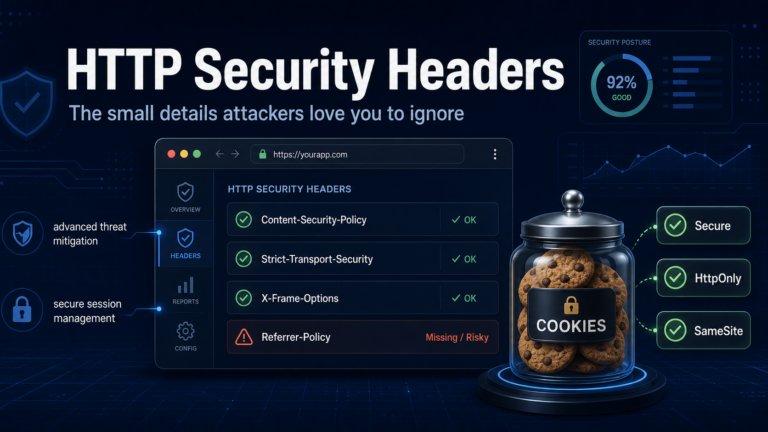
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.
Why running Nmap on Android changes internal recon: faster enumeration from a mobile foothold, realistic constraints, and practical offensive tradecraft.