Nmap on Android (ARM64): Fast Internal Recon from a Mobile Foothold
Tools are not interesting in themselves. What matters is where and how you use them.
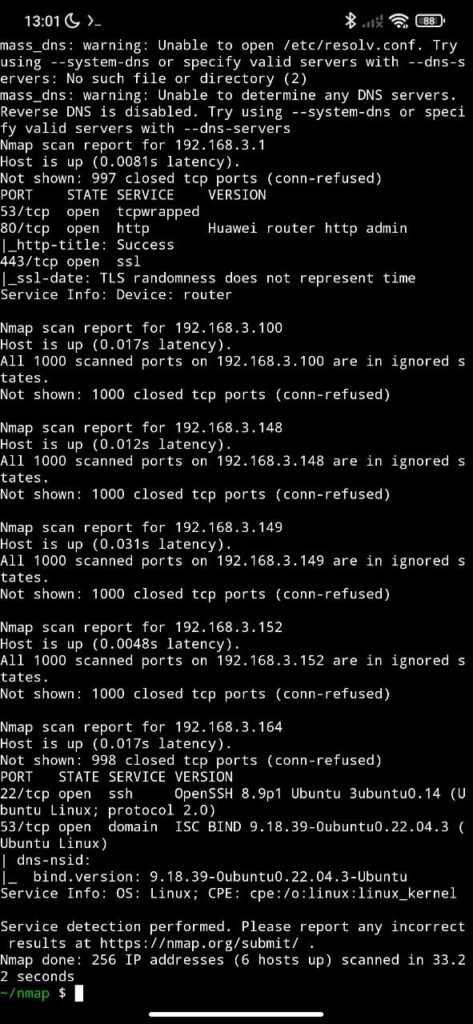
Nmap solved the network discovery problem a long time ago. That is not new. What is still underestimated is the advantage of running it directly from inside the target environment, without depending on external infrastructure.
Real-world context
If you need a laptop to start testing, you are already slow.
In many scenarios, the only device that gets in without friction is the phone. It is already authenticated, it has already passed basic controls, and it usually is not treated as a threat.
That creates an operational blind spot.
Running Nmap directly on Android turns that blind spot into attack surface.
What changes in practice
You are no longer scanning “from the outside.”
You are:
- Inside the corporate Wi-Fi
- Inside a poorly segmented VLAN
- Inside an environment that trusts the device
That drastically reduces the distance to the target.
Host discovery stops being a problem.
Basic enumeration becomes immediate.
No pivot, no tunnel, no setup.
Limitations (and why that does not matter much)
Android was not built for this.
Without root:
- You are limited to TCP connect scans
- Some techniques simply do not work
With root:
- More capability, more precision
- More detection risk depending on the environment
That is not a flaw. It is a characteristic.
You are not trying to replace your attack workstation. You are reducing the time required to get useful signal.
Proper use
This is not for massive scanning.
It is not for running heavy automation.
It is not meant to replace your primary workflow.
It is for:
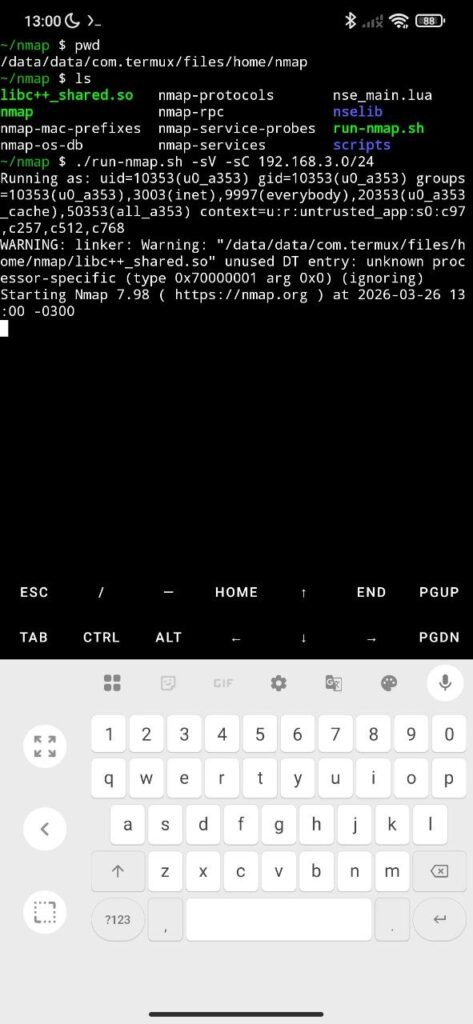
- Quickly identifying what is exposed
- Validating hypotheses inside the network
- Reducing the time between initial access and enumeration
If you can move from “zero visibility” to “I have clear targets” in a few minutes, it has already done its job.
The common mistake
Trying to turn this into a complete solution.
It is not.
It is a rapid-access tool.
If you depend on this for everything, you are operating with the wrong setup.
Repository
Available binaries:
https://github.com/pog007/nmap-android-arm64
It works with and without root. Use it according to the scenario.
Conclusion
The advantage is not in Nmap.
It is in where you run it.
If you are already inside the network, you do not need much to create impact.
💜 Enjoyed this content? Support the blog with USDT (TRC20):
TX7obcjHQbDUXb4mGqoASEu1QFTKT2CFGG