AD CS Containment: Follow the Certificate, Not the Password
A password reset does not revoke an AD CS certificate. Trace ESC1 and ESC8 issuance, validate revocation delivery, and contain existing Kerberos access.

Defensive security guidance covering hardening, validation, monitoring, identity, and secure configuration.
A password reset does not revoke an AD CS certificate. Trace ESC1 and ESC8 issuance, validate revocation delivery, and contain existing Kerberos access.
CVE-2026-103009 let cross-cluster authorization validate one shard identity while execution followed another. Trace the patch, detection, and hardening.
CVE-2026-86060 turned a crafted RouterOS SSH identity into administrative policy. Trace MikroTrick, a safe lab, detection logic, and trusted recovery.
CVE-2026-81963 is an exploited Windows Update link-following flaw. Trace the SYSTEM escalation model, safe mechanism lab, detection logic, and patch validation.
CVE-2026-60004 turns duplicate Gitea diffpatch requests into an executable Git hook. Analyze the attack chain, detection signals, and containment.
Gunra’s locker is the last stage. Detect the earlier handoff from VPN compromise to remote access, exfiltration, backup deletion, and offline encryption.
A macOS ClickFix campaign hid its lure behind browser fingerprinting. This analysis reproduces the gate safely and builds detection across web, endpoint and identity telemetry.
TA488 turned ordinary webmail rendering into browser-resident access. Trace OWAReaper from reading pane to persistence, then hunt its mailbox and browser artifacts.
CVE-2025-68686 is not initial access. It is a FortiOS SSL-VPN symlink patch bypass that turns prior filesystem compromise into remote data exposure.
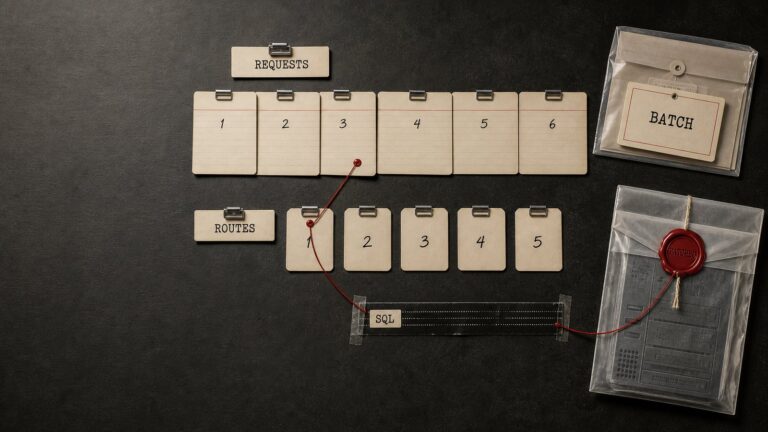
wp2shell chains WordPress REST route confusion with SQL injection to reach pre-auth RCE. Learn the mechanics, affected versions, evidence sources, and safe response workflow.
A real PHP web shell appeared across 47 domains on one shared host. Hunt its signatures, triage WordPress, preserve evidence, and recover safely.
Active SharePoint exploitation demands more than patching. Validate every farm node, hunt IIS and EDR telemetry, rotate trust material, and harden the complete attack path.
OpenSSH 10.3 addresses risks in the SSH client, certificates, forwarding, and legacy scp. Here is the impact, a Blue Team checklist, and safe defensive PoCs.
A practical guide to creating strong passwords with solid cryptography practices and post-quantum readiness. Includes an interactive password generator at the end.
AI as C2 is a real threat in enterprise environments. This guide covers 5 critical risks, detection indicators, and practical defenses for Blue Team.