Shodan.io for Offensive Security: Getting the Most Out of the Internet’s Search Engine
A strange host appears in an exposure report: TCP/8443, a certificate that looks like it belongs to your company, an HTTP title that says “Admin Console”, and a banner that has not changed for months. No one on the infrastructure team recognizes it. The bug bounty team says it is out of scope. The cloud team says it is probably a vendor. The attacker does not care which team owns it.
This is where Shodan is most useful. Not as a magic database of vulnerable targets, but as an external memory of internet-facing services. It shows what the internet can see when nobody is logged into your VPN, nobody has your CMDB, and nobody knows your internal naming conventions.
The mistake I see often is treating Shodan as a search box for “interesting things”. That works for demos. It fails during real reconnaissance, exposure management, and Red Team preparation. To get value from Shodan, you need to think in terms of banners, filters, facets, validation, and operational decision-making.
Shodan searches services, not companies
Shodan’s basic unit is the banner: the response collected from a service on an IP and port. The banner may include protocol text, HTTP headers, TLS certificate data, product names, versions, hostnames, geolocation, organization, ASN, screenshots, and other protocol-specific fields.
This matters because a query like Acme Bank does not mean “show me Acme Bank’s attack surface”. By default, simple terms are matched against banner data. If the value you care about lives in another field — for example the organization name, network range, certificate subject, or hostname — you need filters.
# Too broad and usually misleading
Acme Bank

# Better: search specific structured fields
org:"Acme Bank"
asn:AS64500
hostname:acme.example
ssl.cert.subject.cn:acme.example
net:203.0.113.0/24
The first habit to build is simple: before typing a query, decide which field should prove your hypothesis. If you are mapping ownership, use org:, asn:, net:, hostname:, and certificate fields. If you are mapping technology, use product:, version:, port:, http.title:, http.server:, and protocol-specific fields.
Start with ownership, then pivot into exposure
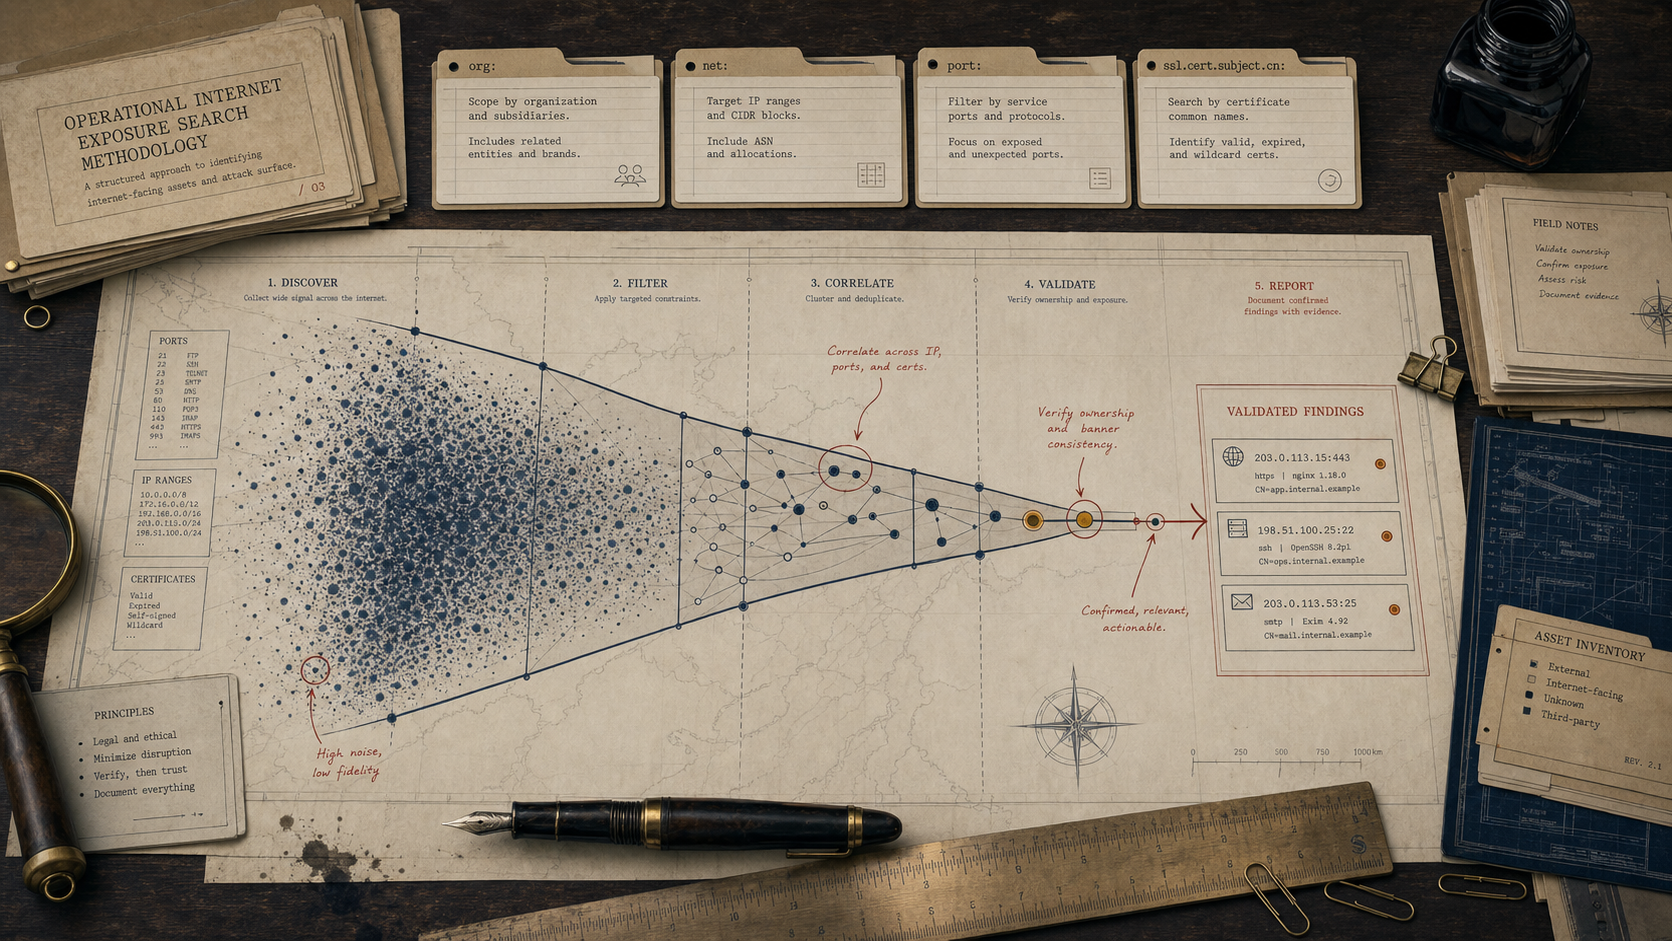
A useful Shodan workflow starts with ownership boundaries. For authorized work, I normally build a small set of seed queries:
# Organization-owned address space
org:"Example Organization"

# Autonomous systems
asn:AS15169

# Known public ranges
net:203.0.113.0/24

# Hostname and DNS-derived exposure
hostname:example.com

# TLS certificate pivots
ssl.cert.subject.cn:example.com
ssl.cert.issuer.cn:"Example Internal CA"
Each seed has blind spots. org: depends on IP allocation data and can miss cloud workloads. hostname: depends on DNS naming. ssl.cert.subject.cn: finds services using relevant certificates, but it can include vendor systems or stale test environments. net: is precise, but only if the asset inventory is precise.
That is why the output should not be treated as truth. Treat it as leads. The defensive value comes from reconciling Shodan evidence with DNS, cloud inventory, EDR telemetry, vulnerability management, certificate transparency, and ownership data.
Use facets before reading individual results
Facets are one of the most underused Shodan features. They summarize a query by properties such as port, organization, ASN, country, product, operating system, or vulnerability. In practice, facets answer questions like:
- Which ports dominate this exposure?
- Which products appear most often?
- Which ASNs or cloud providers are involved?
- Which countries host the unexpected services?
The operational advantage: you can understand the shape of an exposure set before spending time on individual hosts.
# CLI examples
shodan count 'hostname:example.com'
shodan stats --facets port,org,product 'hostname:example.com'
shodan stats --facets port:20,asn:20 'ssl.cert.subject.cn:example.com'

# API count endpoint: returns totals and facets without host results
curl 'https://api.shodan.io/shodan/host/count?query=hostname:example.com&facets=port,org,product&key=$SHODAN_API_KEY'
For large environments, I prefer facet-first triage. If the top ports are 443, 80, and 22, the exposure may be predictable. If RDP, VNC, Redis, Elasticsearch, Jenkins, or management interfaces appear unexpectedly, that becomes a different conversation.
Build queries like hypotheses
Good Shodan queries are not just strings; they are testable assumptions. A few examples:
# Hypothesis: exposed admin panels exist in the owned namespace
hostname:example.com http.title:"admin"

# Hypothesis: SSH is exposed outside expected bastion patterns
hostname:example.com port:22

# Hypothesis: certificates reveal services not visible through DNS naming
ssl.cert.subject.cn:example.com -hostname:example.com

# Hypothesis: old TLS still exists on internet-facing services
hostname:example.com ssl.version:tlsv1

# Hypothesis: a specific product is exposed in the company footprint
org:"Example Organization" product:"Jenkins"

# Hypothesis: screenshots may reveal exposed remote UI surfaces
hostname:example.com has_screenshot:true
The negative operator is especially useful. For example, ssl.cert.subject.cn:example.com -hostname:example.com can reveal certificate reuse on infrastructure that does not carry obvious DNS names. That does not automatically mean compromise or misconfiguration, but it gives you a pivot worth validating.
Know when vuln: is useful — and when it is dangerous
The vuln: filter is attractive because it appears to answer the question everyone wants answered: “Where are the vulnerable systems?” But vulnerability mapping from internet banners is imperfect. Product detection may be wrong. Version extraction may be stale. Backported patches can make version-based assumptions misleading. Reverse proxies can hide the real application behind a generic front end.
# Useful for prioritization, not final proof
hostname:example.com vuln:CVE-2021-41773
org:"Example Organization" vuln:CVE-2023-3519
net:203.0.113.0/24 has_vuln:true
I use vuln: as a triage signal, not as evidence by itself. A finding becomes actionable only after validation against the actual service, patch state, compensating controls, and exploitability in that environment. In a Red Team context, that distinction matters: a stale Shodan banner can waste hours; a validated exposed management plane can change the operation.
Export less, enrich more
Downloading thousands of results feels productive, but large exports become noise quickly. A better approach is to export a narrow result set and enrich it with context.
# Narrow export
shodan download example-ssh 'hostname:example.com port:22'

# Parse only useful fields
shodan parse --fields ip_str,port,org,hostnames,product,version,timestamp example-ssh.json.gz

# Useful fields for triage
ip_str
port
transport
org
asn
hostnames
domains
product
version
http.title
ssl.cert.subject.cn
vulns
timestamp
The timestamp is not cosmetic. Shodan data is collected over time, not continuously on demand for every service. If a banner is old, confirm the exposure before escalating. If a banner is recent and the service is sensitive, prioritize it.
Use the API for repeatable exposure checks
The API is where Shodan becomes part of a workflow instead of a browser tab. For recurring checks, I prefer the /shodan/host/count endpoint with facets when I need trend visibility, and targeted /shodan/host/search calls when I need host-level evidence.
import os
from shodan import Shodan

api = Shodan(os.environ["SHODAN_API_KEY"])

query = 'hostname:example.com port:22,3389,5900'
summary = api.count(query=query, facets='port,org,asn')

print('total:', summary['total'])
for facet, values in summary.get('facets', {}).items():
    print('
' + facet)
    for item in values:
        print(f"  {item['value']}: {item['count']}")
This kind of check can feed a daily exposure digest: new risky ports, new ASNs, unexpected products, or services with vulnerable banners. The key is to alert on meaningful deltas, not raw counts.
A practical Red Team / exposure-management workflow
For authorized assessments, a compact workflow looks like this:
- Define scope: approved domains, netblocks, ASNs, subsidiaries, cloud accounts, and exclusions.
- Seed ownership queries:
org:,asn:,net:,hostname:, certificate pivots. - Run facets: ports, products, ASNs, organizations, countries, vulnerabilities.
- Prioritize: remote access, databases, admin panels, exposed dev/staging, legacy TLS, unusual hosting providers.
- Validate: confirm ownership, freshness, service behavior, and business context.
- Report evidence: banner, timestamp, query, screenshot if available, validation notes, and remediation owner.
- Monitor drift: repeat the query set and alert on meaningful changes.
This is also a good way to keep Red Team reconnaissance defensible. You are not randomly browsing exposed systems; you are testing scoped hypotheses against public metadata and validating only what authorization allows.
What attackers get from Shodan
Attackers use Shodan to reduce uncertainty. They look for technology stacks, exposed management surfaces, forgotten appliances, vulnerable versions, weak segmentation, vendor footprints, and services that should not be internet-facing. The tool does not replace exploitation skill; it improves target selection.
For defenders, the lesson is uncomfortable but useful: if an exposure can be found with a five-minute Shodan query, it should not require a quarterly assessment to discover internally.
Defensive considerations
- Inventory should beat search engines. If Shodan knows more about your edge than your asset inventory, the process is broken.
- Certificate reuse creates pivots. Public TLS metadata can reveal relationships that DNS naming does not.
- Remote access deserves special handling. SSH, RDP, VNC, VPN portals, and appliance management interfaces should have explicit exposure justification.
- Old banners need validation. Do not escalate stale data without checking freshness.
- Monitor changes, not just snapshots. New ports and new providers are often more interesting than the absolute number of exposed services.
Strategic takeaways
Shodan is not valuable because it finds “scary things”. It is valuable because it gives security teams an external, repeatable view of internet exposure. The best operators use it to ask sharper questions:
- What does our organization look like from outside?
- Which services are exposed but not owned by a clear team?
- Which certificates, hostnames, and providers create unexpected pivots?
- Which exposures changed since last week?
- Which findings are validated enough to drive remediation?
For readers building a broader reconnaissance program, this Shodan.io workflow pairs well with the exposure-mapping approach in Defensive Corporate OSINT: A Red Team Guide to Mapping Exposure, Identity, and Cloud.
Shodan.io rewards discipline. Start with ownership, use filters precisely, summarize with facets, validate before escalating, and automate the checks that matter. That is how Shodan moves from curiosity to operational advantage.
References: Shodan Help Center on search query fundamentals and filters; Shodan Developer API documentation for /shodan/host/count, /shodan/host/search, and facets.
💜 Enjoyed this content? Support the blog with USDT (TRC20):
TX7obcjHQbDUXb4mGqoASEu1QFTKT2CFGG