Skip to content
pog0 OffSec
  • Home
  • ToolsExpand
    • My IP: Check Your Public IP (IPv4 & IPv6)
    • Browser Fingerprint: Test and Practical Explanation
    • Secure Password Generator
  • eBooks
  • CheckoutExpand
    • Transaction Failed
    • Confirmation
    • Order History
    • Receipt
  • Links
  • Contact
  • About
pog0 OffSec
  • FeaturedAI Security

    Advanced Threat Modeling: Identities, Trust Boundaries, and Attack Chains

    Advanced threat modeling in practice: identities, trust boundaries, SSRF, cloud metadata, delegated tokens, and blast radius across real attack chains.

    June 17, 202613 min read
    Read article
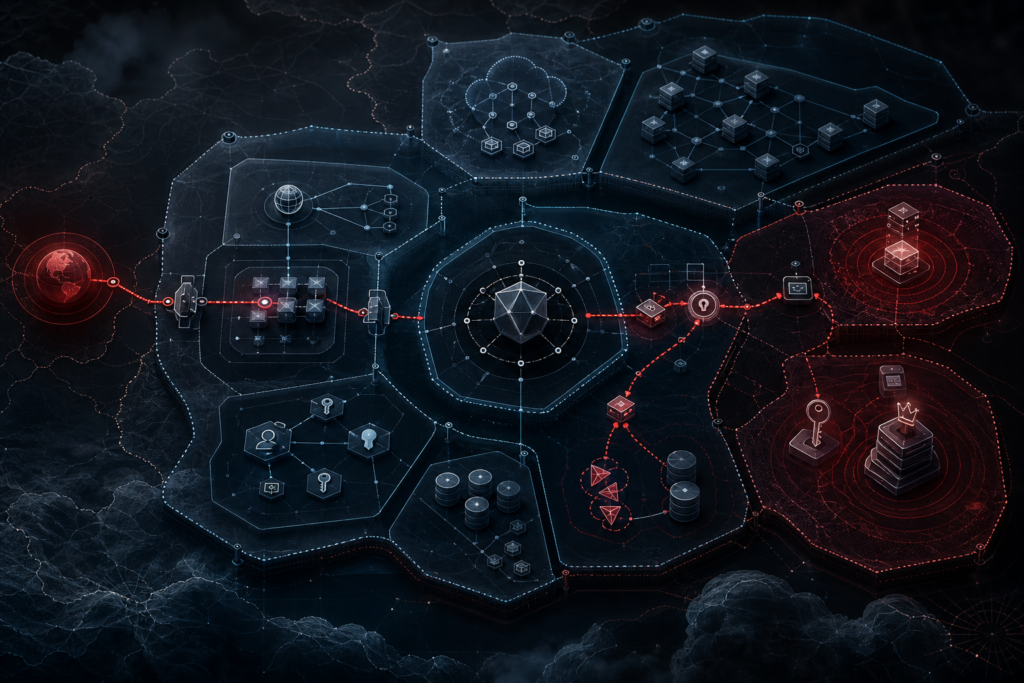
    Featured image about advanced threat modeling with trust boundaries, identities, and attack chains in an offensive security context.
  • Editorial artwork about the five highest-paying vulnerabilities in bug bounty programs.
    Offensive Security | Tools & Labs

    The 5 Highest-Paying Bug Bounty Vulnerabilities

    Bypog0 June 11, 2026June 22, 2026

    The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.

    Read More The 5 Highest-Paying Bug Bounty VulnerabilitiesContinue

  • Featured image about MCP Security, tools, permissions, capability abuse, and Model Context Protocol flows in AI Red Teaming.
    AI Security

    MCP Security: Tools and Permissions in Practice

    Bypog0 June 10, 2026June 21, 2026

    MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
    Read More MCP Security: Tools and Permissions in PracticeContinue

  • Abstract illustration of a safe OpenSSH 9.9 to 10.3 upgrade with SSH keys and a protected access tunnel.
    Defensive Security | News & Analysis

    OpenSSH 9.9 → 10.3: Why You Should Update Now

    Bypog0 June 9, 2026June 21, 2026

    OpenSSH 10.3 addresses risks in the SSH client, certificates, forwarding, and legacy scp. Here is the impact, a Blue Team checklist, and safe defensive PoCs.
    Read More OpenSSH 9.9 → 10.3: Why You Should Update NowContinue

  • Featured image about attacks on embeddings, vector databases, semantic leakage, and sensitive data in an enterprise AI Red Team context.
    AI Security

    Attacks on Embeddings and Vector Databases

    Bypog0 June 8, 2026June 21, 2026

    Embedding attacks in practice: inversion, membership inference, semantic probing, evidence artifacts, and defenses for vector databases.
    Read More Attacks on Embeddings and Vector DatabasesContinue

  • Featured image about AI Red Team failures beyond prompt injection, shown as a forensic evidence board tracing how low-trust input spreads through retrieval, memory, tools, approvals, and actions.
    AI Security

    AI Red Team: 12 Failures Beyond Prompt Injection

    Bypog0 June 5, 2026June 29, 2026

    A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
    Read More AI Red Team: 12 Failures Beyond Prompt InjectionContinue

  • Featured image showing a reconnaissance map for enterprise AI targets, including cloud, AI components, and investigation paths.
    AI Security | Offensive Security

    AI Recon: LLMs, RAGs, and Agents

    Bypog0 June 4, 2026June 22, 2026

    Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
    Read More AI Recon: LLMs, RAGs, and AgentsContinue

  • Featured image about an autonomous pentest agent, represented as a layered technical apparatus that turns reconnaissance into hypotheses, controlled actions, and auditable evidence.
    AI Security | Offensive Security

    Autonomous Pentest Agent: AI, Red Team, and Attack Chains

    Bypog0 June 3, 2026June 29, 2026

    Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
    Read More Autonomous Pentest Agent: AI, Red Team, and Attack ChainsContinue

  • Featured image of an analyst reviewing a graph of corporate exposure, DNS, cloud, identity, APIs, and interconnected trust relationships for OSINT-driven Red Team analysis.
    Offensive Security

    Defensive Corporate OSINT: A Red Team Guide to Mapping Exposure, Identity, and Cloud

    Bypog0 June 2, 2026June 22, 2026

    An advanced guide to defensive corporate OSINT from a Red Team perspective, covering identity, cloud, APIs, detection, and real attack chains.
    Read More Defensive Corporate OSINT: A Red Team Guide to Mapping Exposure, Identity, and CloudContinue

  • Featured image showing Burp Suite-style API request and response analysis with JWT elements, an interceptor workflow, and security validation concepts for API AppSec.
    Offensive Security | Tools & Labs

    Burp Suite Extensions for API Security

    Bypog0 June 1, 2026June 22, 2026

    An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
    Read More Burp Suite Extensions for API SecurityContinue

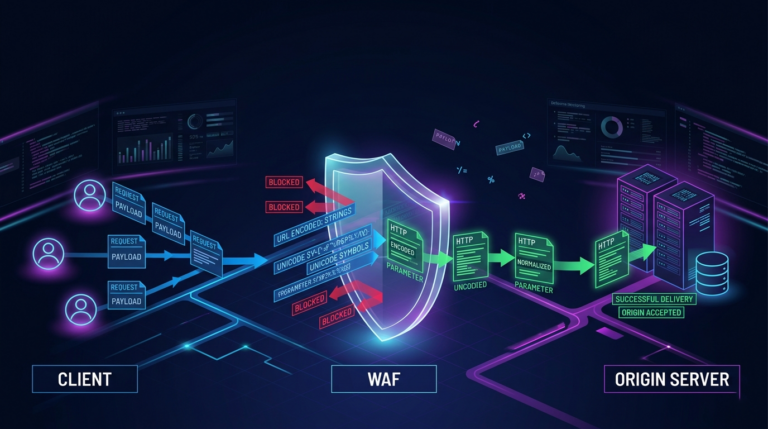
  • WAF bypass traffic flow and normalization gap diagram
    Offensive Security

    WAF Bypass in Practice: Real Techniques, Detection, and Mitigation

    Bypog0 June 1, 2026June 25, 2026

    Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
    Read More WAF Bypass in Practice: Real Techniques, Detection, and MitigationContinue

  • Neon padlock over a keyboard representing strong passwords, entropy, and post-quantum readiness
    Defensive Security | Tools & Labs

    7 Rules for Creating Strong Passwords (+ Generator)

    Bypog0 June 1, 2026June 25, 2026

    A practical guide to creating strong passwords with solid cryptography practices and post-quantum readiness. Includes an interactive password generator at the end.
    Read More 7 Rules for Creating Strong Passwords (+ Generator)Continue

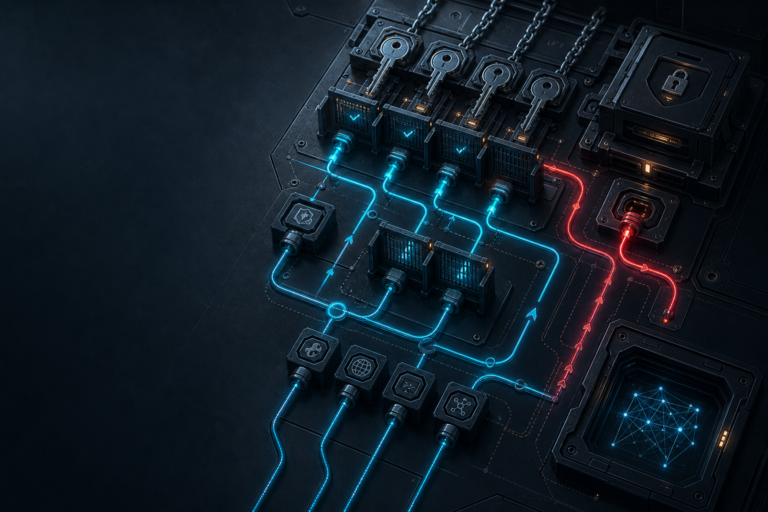
  • Featured image about AI as covert command and control, showing hidden control and exfiltration paths braided inside legitimate encrypted channels with defensive choke points.
    AI Security | Defensive Security

    AI as C2: 5 Risks and Defenses for Blue Team

    Bypog0 May 31, 2026June 29, 2026

    AI as C2 is a real threat in enterprise environments. This guide covers 5 critical risks, detection indicators, and practical defenses for Blue Team.
    Read More AI as C2: 5 Risks and Defenses for Blue TeamContinue

  • Featured image showing a prompt injection metaphor where a syringe labeled prompt injection pierces an AI interface, representing malicious instruction tampering in AI applications.
    AI Security | Defensive Security

    Complete Guide: How to Protect Apps from Prompt Injection

    Bypog0 May 29, 2026June 22, 2026

    Prompt injection is not theoretical. It is a real vulnerability affecting AI applications through direct, indirect, multimodal, and RAG-based attack paths. This guide covers vectors, POCs, evasion techniques, testing, and defenses.
    Read More Complete Guide: How to Protect Apps from Prompt InjectionContinue

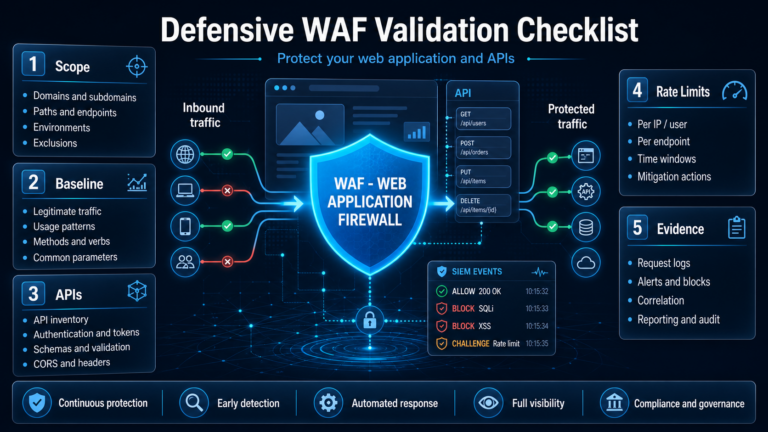
  • Defensive WAF validation checklist infographic for AppSec and Blue Teams showing scope, baseline, APIs, rate limits, evidence, and SIEM events
    Defensive Security | Tools & Labs

    Defensive WAF Validation Checklist for AppSec and Blue Teams

    Bypog0 May 28, 2026June 25, 2026

    A practical checklist for validating WAF coverage safely: scope, evidence, detection, mitigation, rate limits, false positives, and defensive reporting.
    Read More Defensive WAF Validation Checklist for AppSec and Blue TeamsContinue

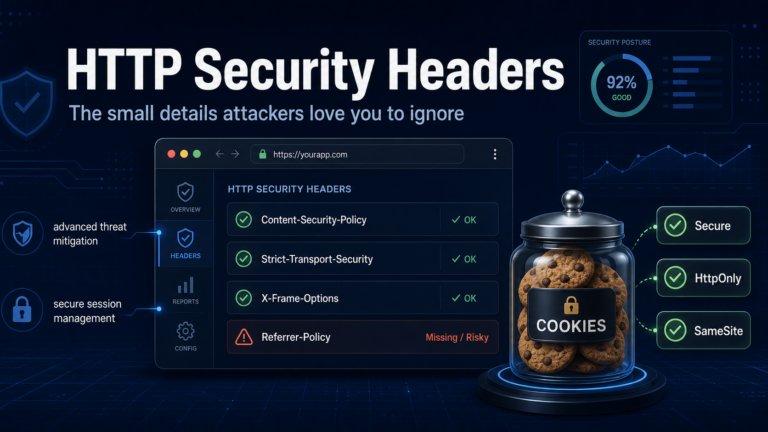
  • HTTP Security Headers featured image showing a browser security panel and cookie protections Secure, HttpOnly, and SameSite
    Defensive Security | Tools & Labs

    HTTP Security Headers: The Small Details Attackers Love You to Ignore

    Bypog0 May 7, 2026June 25, 2026

    Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.
    Read More HTTP Security Headers: The Small Details Attackers Love You to IgnoreContinue

Page navigation

Previous PagePrevious 1 2 3 4 5 Next PageNext

pog0 OffSec

Practical offensive cybersecurity content: pentest, hardening, AI applied to security, VPN, Linux, and tools for Blue Team and Red Team.

About the Author · Contact

Quick Navigation

  • Home
  • Tools
  • Useful Links
  • Support the Project

Tools and Policies

  • My IP
  • Browser Fingerprint
  • Privacy Policy
  • Affiliate Disclosure

© 2026 pog0 OffSec. Technical content for ethical and authorized use.

LinkedIn
LinkedIn
Share
WhatsApp
X (Twitter)
Post on X
Facebook
fb-share-icon

We use cookies to improve your experience on our site. By continuing to browse this site, you agree to the use of cookies.

Privacy Policy
  • Home
  • Tools
    • My IP: Check Your Public IP (IPv4 & IPv6)
    • Browser Fingerprint: Test and Practical Explanation
    • Secure Password Generator
  • eBooks
  • Checkout
    • Transaction Failed
    • Confirmation
    • Order History
    • Receipt
  • Links
  • Contact
  • About