AD CS Containment: Follow the Certificate, Not the Password
A password reset does not revoke an AD CS certificate. Trace ESC1 and ESC8 issuance, validate revocation delivery, and contain existing Kerberos access.

A password reset does not revoke an AD CS certificate. Trace ESC1 and ESC8 issuance, validate revocation delivery, and contain existing Kerberos access.
A privileged workflow can inherit secrets, write tokens, and attacker-controlled artifacts. Learn how to bind the GitHub Actions handoff to immutable evidence.
CVE-2026-97229 lets a crafted CI regular expression reach GitLab native compilation and potentially execute code on the server. Trace the integer-wrap mechanics, patch evolution, safe lab, detection, and control-plane response.
CVE-2026-102870 lets attacker-controlled Blazor application data escape into generated debugger source. This analysis maps the developer-workstation attack chain, a safe mechanism lab, patch scope, and detection opportunities.
PraisonAI exposed a dangerous gap between declared sandbox policy and enforced runtime controls. We trace the agent-to-shell chain, reproduce two mechanics safely, and map the fixes and detections that matter.
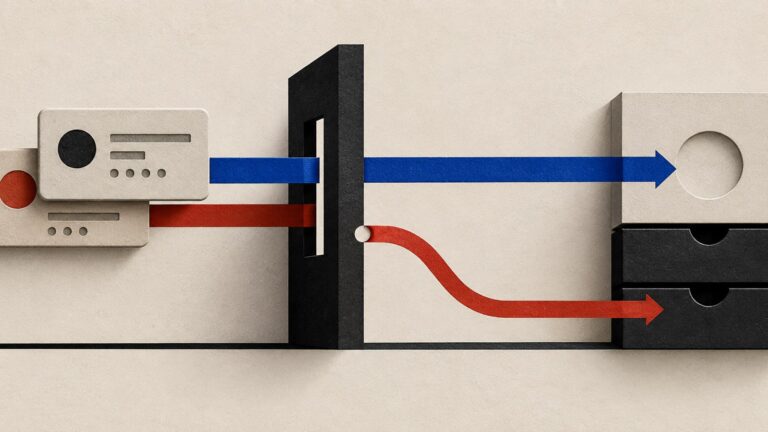
CVE-2026-103009 let cross-cluster authorization validate one shard identity while execution followed another. Trace the patch, detection, and hardening.
CVE-2026-86060 turned a crafted RouterOS SSH identity into administrative policy. Trace MikroTrick, a safe lab, detection logic, and trusted recovery.
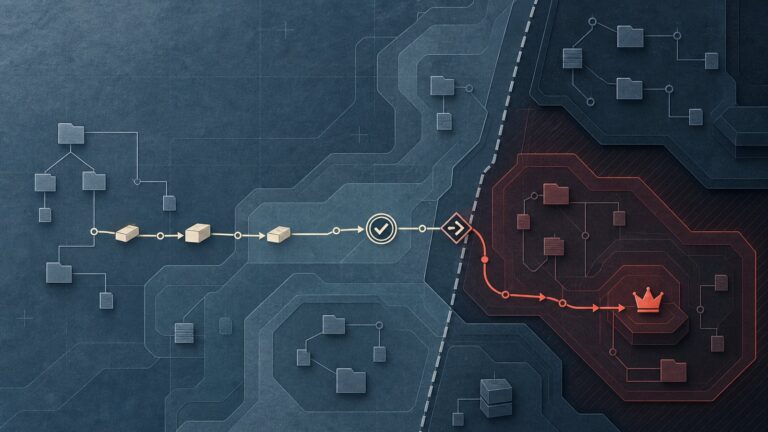
CVE-2026-81963 is an exploited Windows Update link-following flaw. Trace the SYSTEM escalation model, safe mechanism lab, detection logic, and patch validation.
CVE-2026-60004 turns duplicate Gitea diffpatch requests into an executable Git hook. Analyze the attack chain, detection signals, and containment.
ShieldBreak (CVE-2026-69414) abuses file-path resolution around Microsoft Defender. Trace the privilege chain, detection telemetry, and interim controls.
Unit 42’s Pass-ta-key research exposes device-trust and recovery attacks around Google-synced passkeys. Trace the mechanics, detection, and defensive choices.
Gunra’s locker is the last stage. Detect the earlier handoff from VPN compromise to remote access, exfiltration, backup deletion, and offline encryption.
A macOS ClickFix campaign hid its lure behind browser fingerprinting. This analysis reproduces the gate safely and builds detection across web, endpoint and identity telemetry.
CVE-2026-63077 exposes every TeamCity On-Premises version to unauthenticated RCE through the agent polling protocol. This deep dive maps the trust failure, runs a safe deserialization mechanism lab, and shows how to detect, contain, and validate CI/CD integrity.
TA488 turned ordinary webmail rendering into browser-resident access. Trace OWAReaper from reading pane to persistence, then hunt its mailbox and browser artifacts.