CVE-2025-68686: The FortiOS Patch Bypass That Starts After Compromise
CVE-2025-68686 is not initial access. It is a FortiOS SSL-VPN symlink patch bypass that turns prior filesystem compromise into remote data exposure.

CVE-2025-68686 is not initial access. It is a FortiOS SSL-VPN symlink patch bypass that turns prior filesystem compromise into remote data exposure.
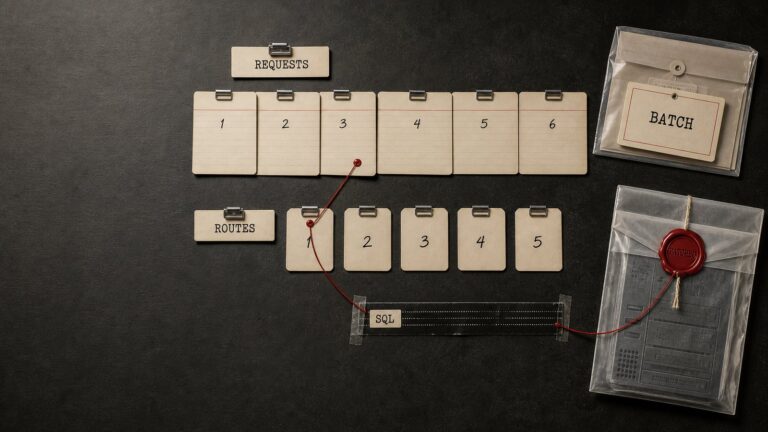
wp2shell chains WordPress REST route confusion with SQL injection to reach pre-auth RCE. Learn the mechanics, affected versions, evidence sources, and safe response workflow.
Active SharePoint exploitation demands more than patching. Validate every farm node, hunt IIS and EDR telemetry, rotate trust material, and harden the complete attack path.
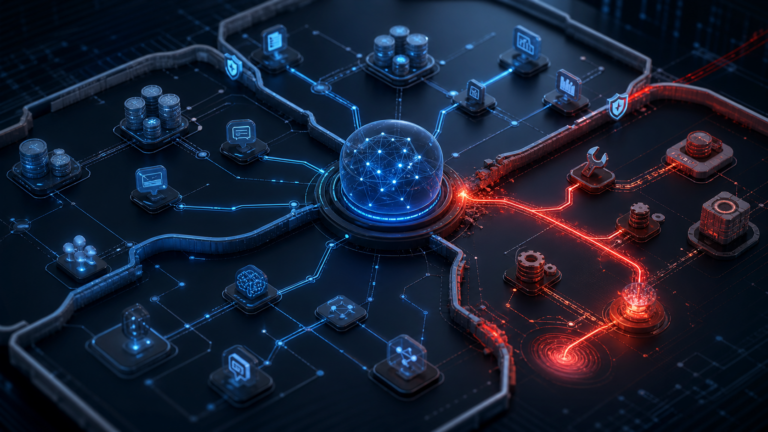
Technical analysis of enterprise AI attack chains: indirect prompt injection, memory poisoning, tool abuse, MCP exposure, and detection.
Advanced guide to AI threat modeling for RAG, agents, and MCP, with trust boundaries, context provenance, and identity separation.
A practical AI Red Team guide to A2A reconnaissance, canary agent registration, agent-card spoofing, and delegation auditing in an authorized lab.
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
Embedding attacks in practice: inversion, membership inference, semantic probing, evidence artifacts, and defenses for vector databases.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
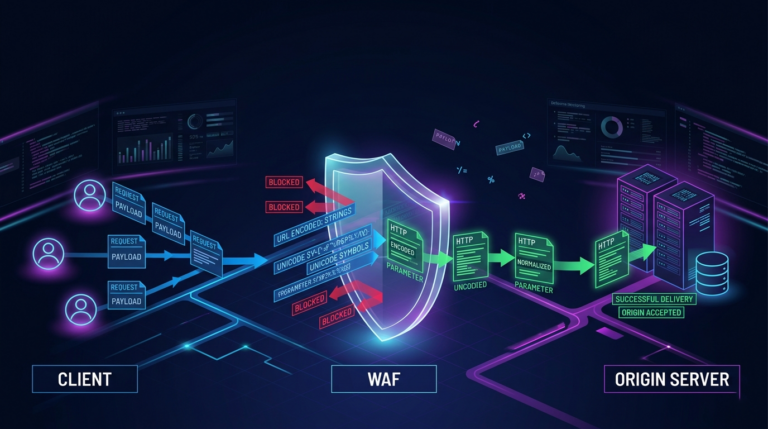
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.