The Link Was Checked Too Late: CVE-2026-81963
CVE-2026-81963 is an exploited Windows Update link-following flaw. Trace the SYSTEM escalation model, safe mechanism lab, detection logic, and patch validation.

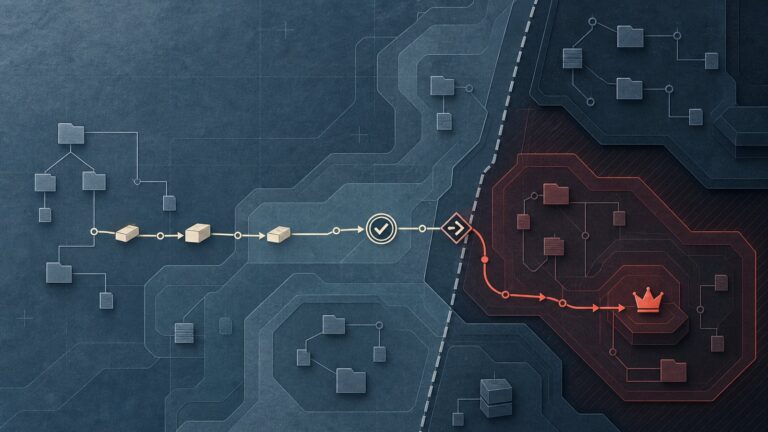
CVE-2026-81963 is an exploited Windows Update link-following flaw. Trace the SYSTEM escalation model, safe mechanism lab, detection logic, and patch validation.
ShieldBreak (CVE-2026-69414) abuses file-path resolution around Microsoft Defender. Trace the privilege chain, detection telemetry, and interim controls.
Practical Shodan.io guide for security teams: build precise queries, use facets, avoid false positives, automate checks, and validate internet exposure.
A practical AI Red Team guide to A2A reconnaissance, canary agent registration, agent-card spoofing, and delegation auditing in an authorized lab.
Agentjacking exploits the blind trust AI assistants place in MCP data. One fake Sentry event and your agent executes malicious code.
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
Embedding attacks in practice: inversion, membership inference, semantic probing, evidence artifacts, and defenses for vector databases.
A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
An advanced guide to defensive corporate OSINT from a Red Team perspective, covering identity, cloud, APIs, detection, and real attack chains.
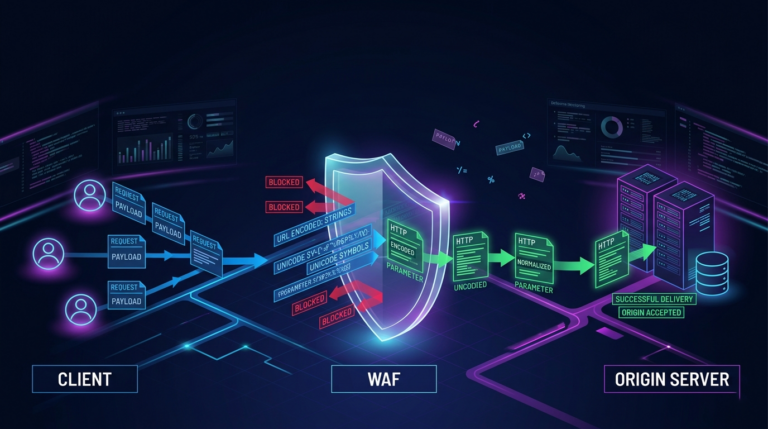
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
Prompt injection is not theoretical. It is a real vulnerability affecting AI applications through direct, indirect, multimodal, and RAG-based attack paths. This guide covers vectors, POCs, evasion techniques, testing, and defenses.
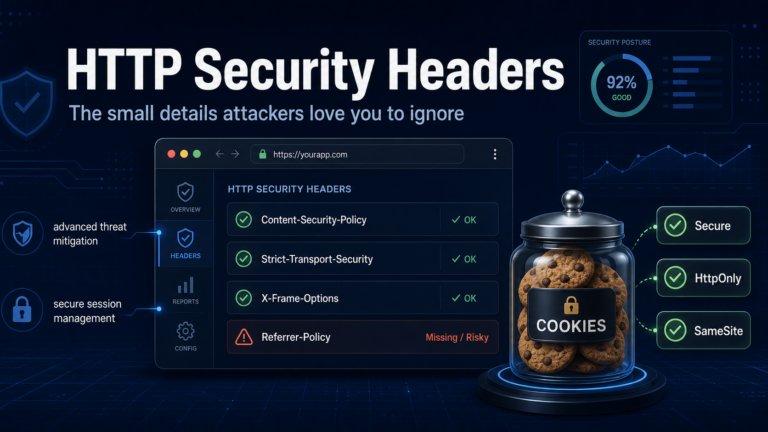
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.







