The Constructor Was the Endpoint: Jenkins Stapler Data Binding
Jenkins configuration forms can become constructor dispatch. Trace the September 2026 flaws, a safe mechanism lab, detection signals, and durable fixes.

Jenkins configuration forms can become constructor dispatch. Trace the September 2026 flaws, a safe mechanism lab, detection signals, and durable fixes.
ShieldBreak (CVE-2026-69414) abuses file-path resolution around Microsoft Defender. Trace the privilege chain, detection telemetry, and interim controls.
Unit 42’s Pass-ta-key research exposes device-trust and recovery attacks around Google-synced passkeys. Trace the mechanics, detection, and defensive choices.
CVE-2026-63077 exposes every TeamCity On-Premises version to unauthenticated RCE through the agent polling protocol. This deep dive maps the trust failure, runs a safe deserialization mechanism lab, and shows how to detect, contain, and validate CI/CD integrity.
Frida remains valuable in Android assessments, but it is most useful when used to validate runtime hypotheses instead of blindly bypassing every control in the app.
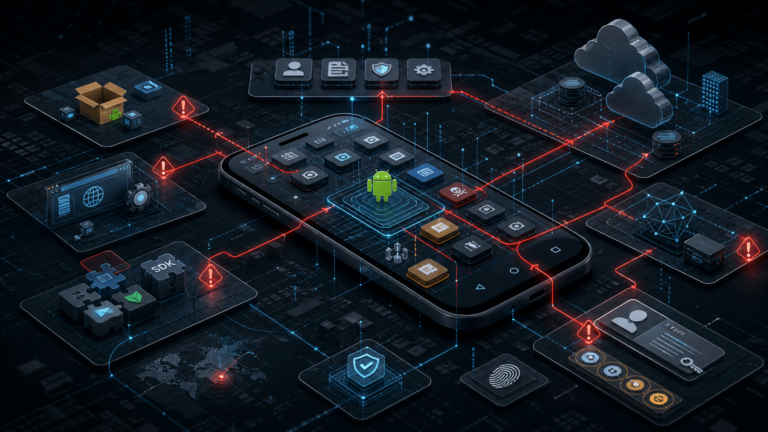
Android security research still pays off, but the best bugs now sit across APK logic, identity flows, backend APIs, SDK trust boundaries, WebView surfaces, and abuse-resistant controls such as attestation.
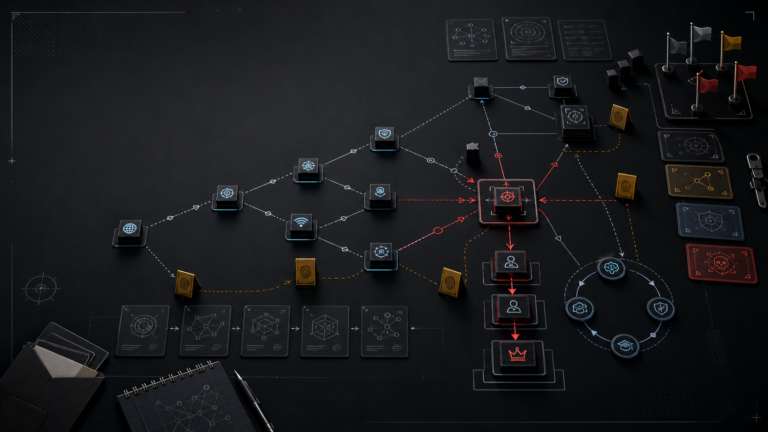
How to use ethical hacking labs to train enumeration, exploitation, evidence gathering, and reporting discipline without falling into CTF habits.
The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
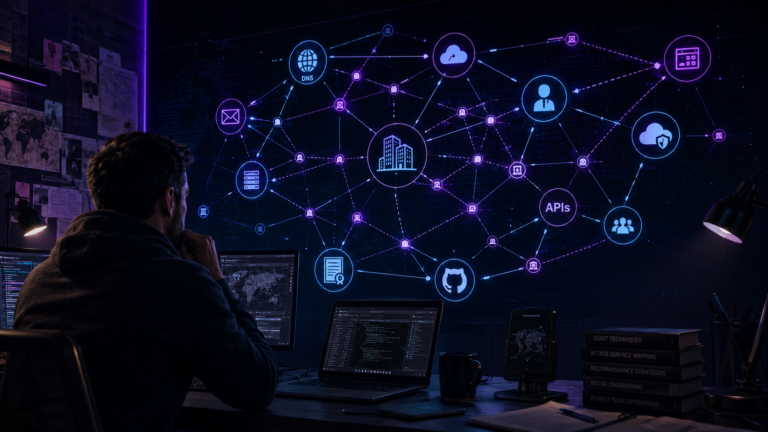
An advanced guide to defensive corporate OSINT from a Red Team perspective, covering identity, cloud, APIs, detection, and real attack chains.
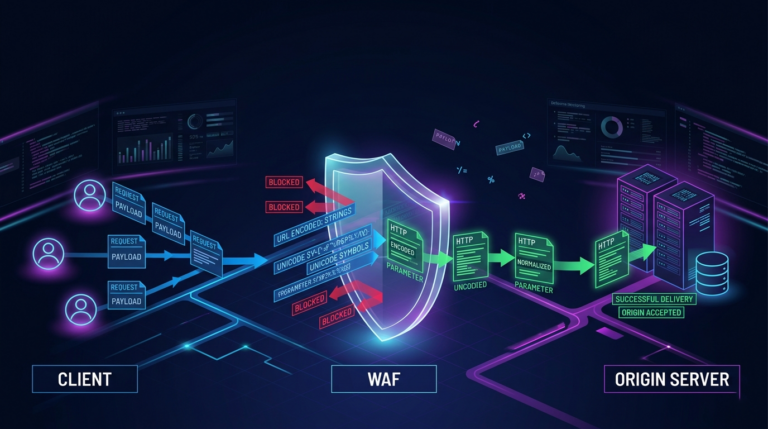
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
AI as C2 is a real threat in enterprise environments. This guide covers 5 critical risks, detection indicators, and practical defenses for Blue Team.







