The Android Attack Surface in 2026: What Still Matters for Offensive Security
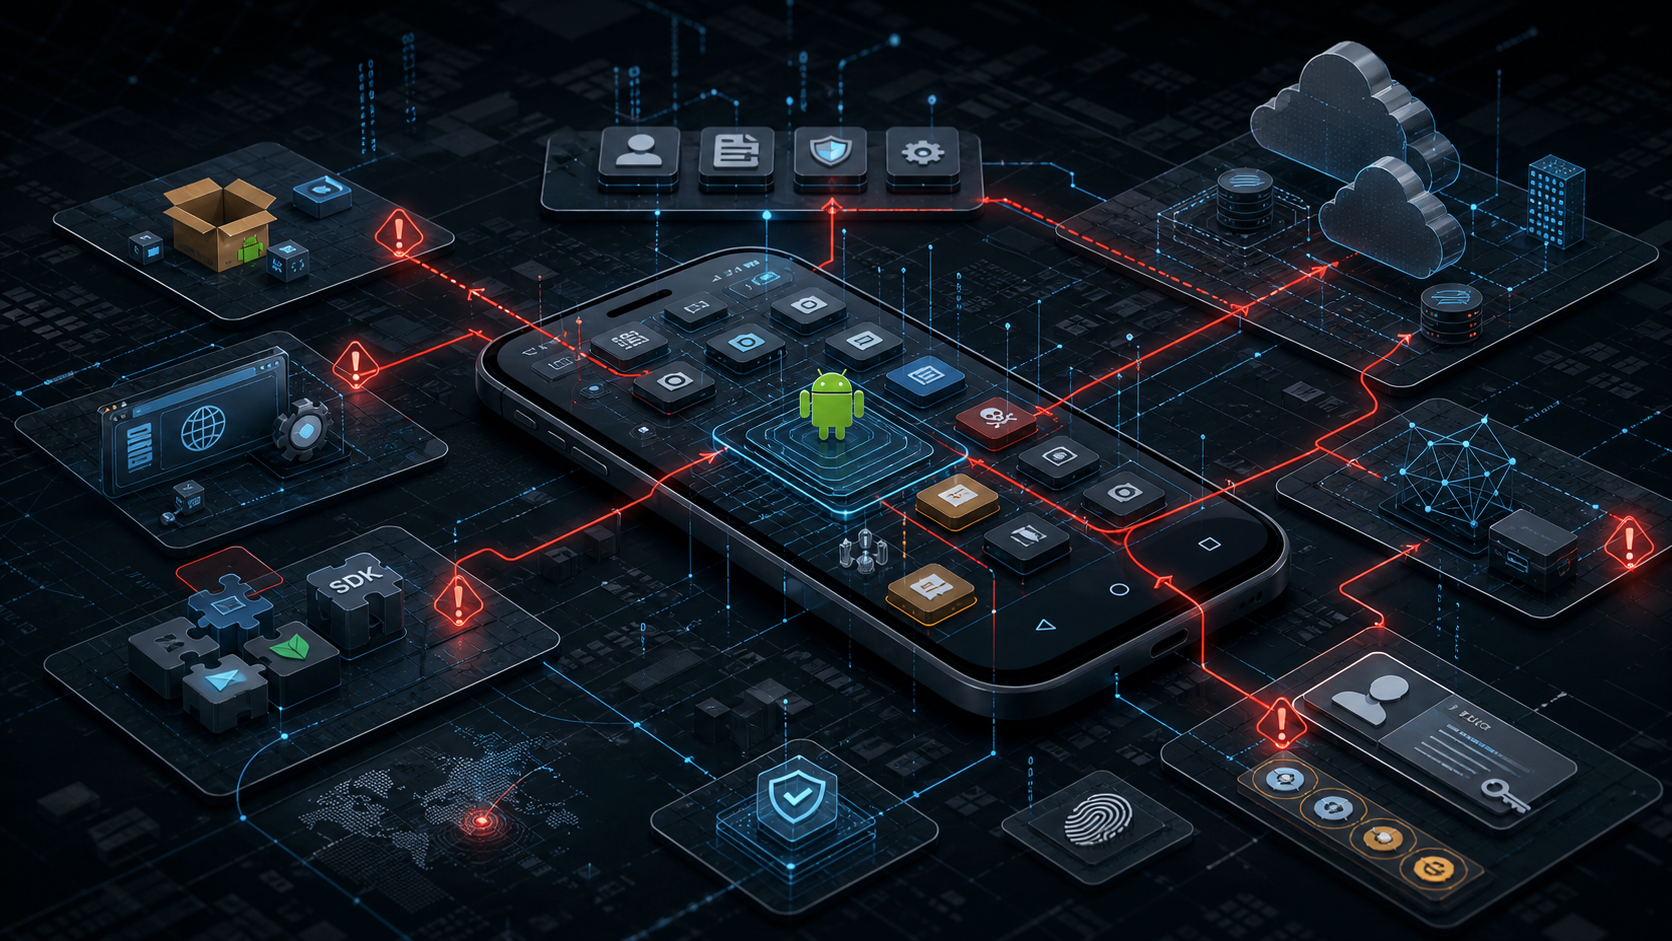
Android security research still pays off, but the best bugs now sit across APK logic, identity flows, backend APIs, SDK trust boundaries, WebView surfaces, and abuse-resistant controls such as attestation.
Why Android still matters
Android is not interesting because it is exotic. It is interesting because it is operationally close to money, identity, enterprise access, and high-frequency user behavior. Banking apps, wallets, MFA clients, workforce tools, healthcare portals, delivery platforms, and internal enterprise apps all carry security assumptions that often extend far beyond the APK.
For offensive security, that makes Android less of a standalone mobile target and more of a client-side entry point into a larger business system. A weak exported component may be the first observable issue, but the real impact is often unauthorized account actions, API abuse, device binding bypass, session theft, or fraud workflow manipulation.
What changed
The platform keeps hardening. Android 16 documentation explicitly calls out security changes such as improved protection against Intent redirection attacks, and Android’s release cadence continues to push behavior changes, privacy restrictions, runtime updates, and compatibility pressure into the ecosystem. Google Play also keeps moving more security decisioning into signing, integrity, policy, and distribution controls.
This matters because old mobile testing habits age badly. A checklist that stops at static APK review misses the systems that actually decide trust: backend risk engines, Play Integrity responses, OAuth flows, third-party SDK behavior, remote configuration, feature flags, and device registration state.
The other important change is architectural. Many Android apps are now thin clients for server-driven product logic. That shifts part of the attack surface from local code to protocol sequencing, state handling, and business authorization.
What still breaks in real apps
The reliable findings have not disappeared; they have moved into combinations. Exported activities, services, receivers, and content providers still create entry points when intent filters, permissions, and assumptions about caller identity are weak. Deep links still route untrusted input into sensitive flows. WebViews still collapse origin boundaries when native bridges, file access, or navigation handling are too permissive.
Sensitive local storage is still found in SQLite databases, shared preferences, logs, cache directories, screenshots, WebView storage, and SDK-managed stores. Client-side secrets still appear in resources, native libraries, remote config defaults, and analytics integrations. Certificate pinning is still misimplemented or treated as a complete control rather than a delay mechanism.
Most importantly, authorization logic still leaks into the client. If the app decides whether a user can see, trigger, approve, or modify something without equivalent server-side enforcement, the Android client becomes a convenient oracle for business logic flaws.
Where offensive research should focus now
The best Android assessments in 2026 should prioritize chains, not isolated primitives. Start with identity flows: OAuth redirect handling, PKCE usage, token refresh logic, account switching, device binding, session revocation, and recovery flows. Then test whether the backend treats device claims, app claims, and user claims as independent trust inputs or blindly accepts the client narrative.
Attestation deserves special attention. Play Integrity is useful, but it is not a substitute for authorization. The server should treat integrity verdicts as risk signals with freshness, replay resistance, nonce binding, and action-specific decisioning. If the result can be replayed, cached too broadly, evaluated only on login, or disconnected from the sensitive action, the control becomes weaker than its architecture diagram suggests.
Third-party SDKs are another under-tested area. Analytics, attribution, ads, chat, identity verification, fraud prevention, and payment SDKs often introduce storage, WebView, networking, and lifecycle behavior that the app team does not fully model. The SDK is part of the attack surface even when it is not owned by the app team.
Practical testing stack in 2026
A practical mobile security stack is still simple: adb for device control, jadx and apktool for static analysis, Frida for runtime inspection, Burp Suite or mitmproxy for traffic analysis, MobSF for quick triage, and a mix of emulator and physical-device testing.
The difference is how the tools are used. Static analysis should produce hypotheses, not final answers. Dynamic instrumentation should validate security decisions at runtime. Proxying should map authorization and state transitions, not merely collect endpoints. Physical devices matter for biometrics, Play services, hardware-backed keys, root-detection behavior, and OEM-specific differences. Emulators remain useful for repeatability and fast iteration.
What I will publish next
This post is the start of a focused Android return series. The next pieces will go deeper into WebView trust boundaries, Frida usage in real assessments, deep link abuse, and testing Android authentication flows beyond the APK. The goal is not to recycle mobile pentest checklists. The goal is to document where Android security work still produces meaningful findings.
References
- Android 16 features and changes list
- Play Integrity API
- Android security overview
- Android Offensive Security Blog
💜 Enjoyed this content? Support the blog with USDT (TRC20):
TX7obcjHQbDUXb4mGqoASEu1QFTKT2CFGG