Android App Security: Root Detection, Frida, and the Failure of Client-Side Trust
⚠️ Test only apps and environments you own or are explicitly authorized to assess. The examples and defensive guidance below are intended for legitimate mobile application security reviews.
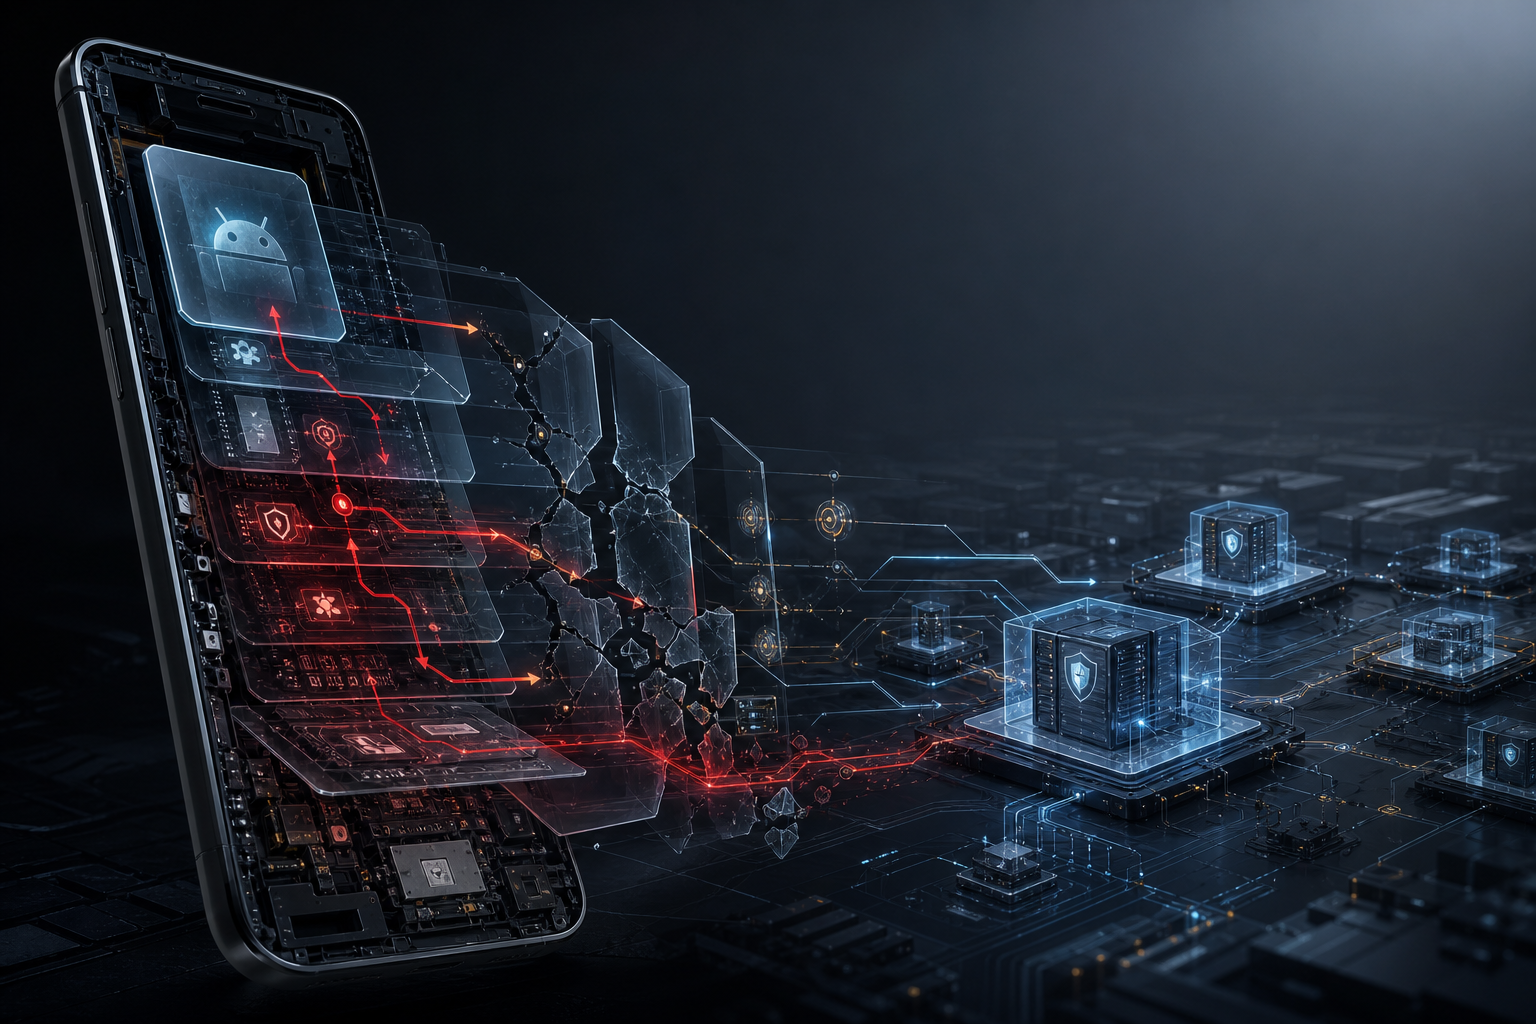
Executive summary: Android app security is often discussed in terms of root detection, anti-Frida logic, emulator checks, and runtime attestation. Those controls matter, but they are not where most high-impact failures start. The bigger problem is misplaced trust: business logic, authorization decisions, secrets, and sensitive workflows are still too often exposed to a device the user fully controls. Root checks and environment validation can raise attacker cost, but they do not fix broken trust boundaries.
- Use when: reviewing an Android app that handles sensitive data, payment logic, identity workflows, proprietary algorithms, or high-value API access.
- Avoid: treating root detection, Frida detection, or Play Integrity as substitutes for server-side authorization and cryptographic verification.
- Expected deliverable: evidence showing which controls are enforcement points, which are only telemetry signals, and whether compromise of the mobile client can materially change backend outcomes.
The real problem: the APK runs on an attacker-controlled device
Every Android security discussion should start with one operational fact: once the APK is delivered to a user device, the defender no longer controls the execution environment.
A capable analyst can usually:
- extract and reverse the APK;
- inspect Java/Kotlin bytecode and native libraries;
- instrument methods at runtime with Frida or equivalent tooling;
- patch logic statically and re-sign the APK;
- run the app on rooted devices, custom ROMs, emulators, or repackaged environments.
This is why mobile security is fundamentally different from traditional server-side security. On the server, you can often trust your own runtime. On mobile, you cannot. Any design that assumes the client is an authoritative enforcement point is already in a weak position.
1. Excessive trust in client-side authorization and business logic
This is still the most consequential Android application weakness.
In mature attacks, the objective is rarely “bypass root detection” for its own sake. The objective is to alter a trusted workflow:
- unlock premium features;
- manipulate transaction parameters;
- bypass anti-abuse logic;
- replay or forge API requests;
- disable local fraud checks;
- change identity or entitlement decisions before they reach the backend.
What this looks like in practice
Common patterns include:
- role or entitlement checks enforced only in the app;
- prices, discounts, balances, or limits computed locally and weakly validated server-side;
- feature flags or internal endpoints hidden only by UI logic;
- tokens, device identifiers, or request-signing material exposed in the client;
- local “allow/deny” decisions later accepted by the backend as if they were trustworthy.
Why root checks do not solve this
If the backend accepts a manipulated request, then the real vulnerability is server trust, not the absence of local anti-tamper logic.
This is the same reason API security reviews need evidence-driven validation rather than UI-level assumptions. If you want a backend-focused companion piece, see Burp Suite Extensions for API Security, which covers how to turn recurring authorization and logic hypotheses into controlled AppSec checks.
Root detection may stop unsophisticated abuse on some devices. It does not stop:
- repackaging;
- method hooking on supported or hidden environments;
- traffic replay from extracted tokens;
- server-side abuse using values learned from the app.
What good looks like
- Treat the Android app as a presentation and collection layer, not as a policy authority.
- Recompute sensitive decisions on the backend.
- Bind authorization to authenticated server-side state.
- Sign or attest only what the server can independently verify.
- Make fraud and access decisions resilient to complete compromise of the client.
2. Insecure local storage and recoverable secrets
The second recurring problem is assuming that data stored on the device is private because it is “inside the app”.
That assumption breaks quickly during a mobile assessment. Sensitive values often end up in:
- SharedPreferences;
- SQLite or Realm databases;
- cached API responses;
- logs and crash traces;
- WebView storage;
- exported backups;
- temporary files on shared or external storage.
Why this matters operationally
Attackers do not always need full code execution. Sometimes they only need to recover:
- session tokens;
- refresh tokens;
- API keys;
- user identifiers;
- feature flags;
- cryptographic material incorrectly stored next to ciphertext;
- personally identifiable information.
Once recovered, these values can support account takeover, replay, fraud, or high-fidelity reverse engineering of backend behavior.
Defensive direction
- Minimize what is stored locally.
- Keep secrets out of logs and crash paths.
- Do not place sensitive data in external storage.
- Use the Android Keystore for keys, but remember that secure key storage does not automatically make the surrounding workflow secure.
- Design tokens and sessions so that theft from one device has bounded impact.
3. Unsafe exported components and deep-link entry points
Android apps often expose activities, services, receivers, or content providers more broadly than intended. Deep-link handlers create similar risk when input validation is weak.
Typical failure modes
- exported activities reachable without proper preconditions;
- internal flows accessible directly via crafted intents;
- deep-link parameters accepted without strict allowlisting;
- authenticated screens exposed through navigation shortcuts;
- content providers leaking internal records;
- intent redirection that forwards attacker-controlled extras into privileged components.
Impact
This class of issue can produce:
- unauthorized access to internal functionality;
- sensitive data leakage;
- privilege misuse inside the app context;
- phishing or state-confusion flows;
- chaining into WebView or native bridge abuse.
Why it is often underestimated
Teams frequently focus on network traffic and miss the fact that Android components are another attack surface. In real reviews, local inter-app attack paths can be enough to expose internal screens, bootstrap account workflows, or deliver attacker-controlled content to privileged code paths.
Defensive direction
- Explicitly define
android:exportedfor every component. - Protect sensitive components with permissions and state checks.
- Validate all deep-link parameters as untrusted input.
- Check authentication and authorization again at the receiving component.
- Sanitize forwarded intents instead of relaying them blindly.
4. WebView misuse and JavaScript bridge exposure
WebView remains one of the richest Android attack surfaces because it combines web problems with native privileges.
High-risk patterns
- loading attacker-influenced URLs into privileged WebViews;
- enabling JavaScript where it is not necessary;
- exposing
addJavascriptInterfacebridges to untrusted content; - allowing unsafe file access from
file://contexts; - mixing deep links, untrusted navigation, and native bridge methods;
- leaving debugging or permissive settings enabled in production builds.
Why this is dangerous
A WebView is not just a browser tab. If the host app exposes bridge methods or privileged session context, a web-origin issue can become a native-app issue.
That can lead to:
- sensitive data extraction;
- UI redirection to phishing content;
- invocation of native functions from attacker-controlled JavaScript;
- abuse of file access permissions;
- escalation from XSS-like primitives into app-level compromise.
Defensive direction
- Disable JavaScript unless the feature strictly requires it.
- Never expose powerful bridge methods to untrusted origins.
- Remove JavaScript interfaces before loading untrusted content.
- Prefer safer local content patterns such as
WebViewAssetLoaderinstead of permissive file access. - Treat every URL, redirect, and message crossing the WebView boundary as untrusted input.
5. Misunderstanding root detection, Frida detection, and environment validation
This is where many mobile security discussions become confused.
Root checks, anti-debugging, anti-hooking, emulator detection, and runtime attestation are useful resilience controls. They are not primary security boundaries.
That distinction matters.
Root detection
Root detection tries to identify whether the app runs on a rooted or modified device. OWASP MASTG is explicit here: the goal is to make running the app on a rooted device more difficult, not impossible. OWASP also notes that root detection is not very effective by itself and becomes more meaningful only when multiple checks are scattered across the app as part of a larger anti-tampering design.
Typical checks include:
subinary presence;- Magisk- or root-related packages;
- writable system partitions;
- suspicious mount points;
- test keys or custom ROM indicators.
Frida and hook detection
Frida changes the economics of Android assessment because it lets an analyst instrument methods, alter return values, intercept crypto usage, and inspect runtime state without fully rebuilding the app.
Teams therefore add detections such as:
- scanning
/proc/self/mapsfor Frida-related artifacts; - checking suspicious ports or process names;
- looking for known gadget strings;
- anti-debug or anti-trace checks;
- integrity checks on classes or native libraries.
The problem is not that these controls are useless. The problem is assuming they are decisive. OWASP MASTG includes demonstrations where a hook-detection mechanism that scans /proc/self/maps and kills the process can still be bypassed by hooking BufferedReader.readLine() so Frida-related entries are hidden from the app itself.
Environment validation and attestation
Google Play Integrity and hardware-backed key attestation improve signal quality substantially compared with purely local checks. They can help distinguish:
- whether the binary matches what Google Play recognizes;
- whether the device meets integrity conditions;
- whether the environment looks risky or emulated;
- whether hardware-backed key material can be verified by a trusted backend.
These are useful controls, especially against fraud and automation. But they still need correct architecture:
- validation must happen off-device;
- backend decisions must treat attestation as one signal among several;
- fallback logic must not silently accept unverifiable states;
- the app must fail safely when integrity evidence is missing, weak, or inconsistent.
If you want to compare mobile environment signals with browser-side telemetry, Browser Fingerprint: Test and Practical Explanation is a useful adjacent reference on paulo.seg.br. The threat model is different, but the same lesson applies: environment evidence can inform risk decisions, yet it should not be confused with identity or trust by itself.
The architectural rule
If bypassing root or Frida detection immediately gives an attacker material access to backend privileges, money movement, or sensitive data, then the environment checks were covering for a deeper design problem.
6. Weak cryptographic boundaries and local-only trust anchors
Many Android apps use encryption, but not always in a way that changes attacker outcomes.
Common mistakes
- hardcoded keys or predictable derivation logic in the APK;
- decrypting high-value material entirely on the client with no server control;
- using encryption only to hide strings from casual inspection;
- performing signature verification locally without an independent server trust anchor;
- storing the protected data and the means to recover it on the same compromised device.
Operational reality
If an attacker can instrument the moment plaintext appears in memory, then local encryption by itself may only slow analysis. That is still useful in some threat models, but teams should be honest about what it buys.
Defensive direction
- Use cryptography to enforce server-recognized trust decisions, not just to obscure implementation details.
- Keep verification logic off-device when possible.
- Protect keys with hardware-backed facilities where available, then verify attestation and certificate chains on a trusted backend.
- Plan for runtime compromise and measure whether the design still contains blast radius.
A practical way to think about Android mobile risk
A useful Android app security review sequence is:
- What can the backend still trust if the client is fully instrumented?
- What data, keys, or workflows become dangerous if the device is rooted?
- What changes if the app is repackaged or patched?
- Can deep links, exported components, or WebViews reach privileged code paths?
- Are root/Frida checks enforcing anything, or only generating telemetry?
- Does the app degrade safely when integrity evidence is absent?
This sequence tends to separate cosmetic hardening from controls that actually change attacker cost and business impact.
What mature Android hardening looks like
A strong Android security posture usually has the following properties:
Server-side trust is primary
- authorization is enforced on the backend;
- business-critical values are recomputed or verified server-side;
- mobile signals enrich risk scoring but do not replace core policy decisions.
Resilience controls are layered
- root, hook, debug, and emulator checks exist in multiple places;
- integrity checks cover both Java/Kotlin and native paths where justified;
- telemetry is tied to meaningful server responses.
Data exposure is minimized
- local storage is treated as recoverable by a determined analyst;
- tokens and secrets are scoped, rotated, and monitored;
- high-value data is not retained longer than necessary.
Attack surfaces are deliberately reduced
- exported components are minimal and explicit;
- deep links are strictly validated;
- WebViews are constrained, origin-aware, and bridge-safe.
Final assessment
The most important Android app security failures are not the easiest controls to list in a slide deck.
A missing root check is visible. A missing Frida detection routine is visible. An absent emulator block is visible.
But the larger failures are usually less cosmetic:
- a backend trusting values computed on the device;
- a session token recoverable from local storage;
- a deep link that reaches a privileged state transition;
- a WebView bridge exposed to attacker-influenced content;
- an attestation result verified on the same device the attacker already controls.
Root detection, Frida detection, and environment validation still matter. They can increase cost, improve telemetry, and reduce commodity abuse. They are worth implementing when the threat model justifies them.
They just should not be confused with the security boundary itself.
If the app remains safe after those controls fail, the architecture is probably sound.
If everything collapses when those controls fail, the architecture was relying on the wrong layer.
References
- Android Developers — Overview of the Play Integrity API
- Android Developers — Verify hardware-backed key pairs with key attestation
- Android Developers — WebViews – Unsafe File Inclusion
- Android Developers — WebView – Native bridges
- Android Developers — Unsafe use of deep links
- Android Developers — android:exported
- Android Developers — Security checklist
- OWASP MASTG — MASTG-KNOW-0027: Root Detection
- OWASP MASTG — MASTG-DEMO-0108: Bypassing Frida Detection in /proc/self/maps to Extract Sensitive Data
💜 Enjoyed this content? Support the blog with USDT (TRC20):
TX7obcjHQbDUXb4mGqoASEu1QFTKT2CFGG