The Username Was a File Descriptor: Inside MikroTrick
CVE-2026-86060 turned a crafted RouterOS SSH identity into administrative policy. Trace MikroTrick, a safe lab, detection logic, and trusted recovery.

CVE-2026-86060 turned a crafted RouterOS SSH identity into administrative policy. Trace MikroTrick, a safe lab, detection logic, and trusted recovery.
CVE-2026-60004 turns duplicate Gitea diffpatch requests into an executable Git hook. Analyze the attack chain, detection signals, and containment.
Gunra’s locker is the last stage. Detect the earlier handoff from VPN compromise to remote access, exfiltration, backup deletion, and offline encryption.
A macOS ClickFix campaign hid its lure behind browser fingerprinting. This analysis reproduces the gate safely and builds detection across web, endpoint and identity telemetry.
TA488 turned ordinary webmail rendering into browser-resident access. Trace OWAReaper from reading pane to persistence, then hunt its mailbox and browser artifacts.
CVE-2025-68686 is not initial access. It is a FortiOS SSL-VPN symlink patch bypass that turns prior filesystem compromise into remote data exposure.
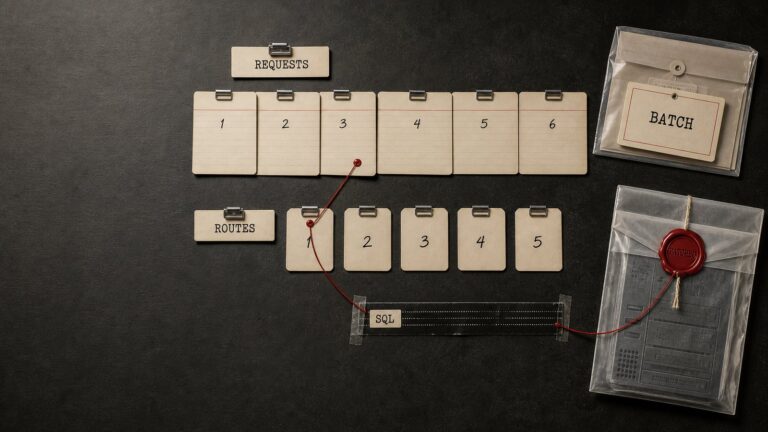
wp2shell chains WordPress REST route confusion with SQL injection to reach pre-auth RCE. Learn the mechanics, affected versions, evidence sources, and safe response workflow.
A real PHP web shell appeared across 47 domains on one shared host. Hunt its signatures, triage WordPress, preserve evidence, and recover safely.
Active SharePoint exploitation demands more than patching. Validate every farm node, hunt IIS and EDR telemetry, rotate trust material, and harden the complete attack path.
A practical guide for security teams on when public ransomware decryptors work, where to find them, and how to avoid making recovery worse.