WebView Is Still a Mess: Android Hybrid Apps Keep Repeating the Same Security Mistakes
WebView remains one of the most productive Android AppSec targets because hybrid apps repeatedly mix trusted native capabilities with untrusted or weakly controlled web content.
Why WebView keeps producing bugs
WebView is attractive because it compresses product delivery: one web surface can be reused inside Android, iOS, and sometimes desktop flows. The security problem is that WebView also compresses trust boundaries. It can make remote content feel native, expose native capabilities to JavaScript, persist sensitive web state inside the app, and route external input into authenticated user sessions.
Android’s documentation is clear that WebView is not a full browser. It lacks browser UI such as an address bar and navigation controls. That means users get fewer cues about origin, navigation, and trust, while developers often assume the embedded surface is safer than it really is.
The dangerous bridge: JavaScript to native
The classic failure mode is still a JavaScript bridge that exposes native methods to pages that should not be trusted with native authority. On modern Android, methods need the @JavascriptInterface annotation to be exposed, which avoids some historical reflection abuse. That does not make the design safe. It only narrows the mechanics.
If a WebView can navigate to attacker-controlled content, or if trusted content can be script-injected, every exposed bridge method becomes part of the attack surface. The right question is not “is addJavascriptInterface patched?” The right question is “which origins can reach this capability, and what can they do once they reach it?”
Navigation and origin control
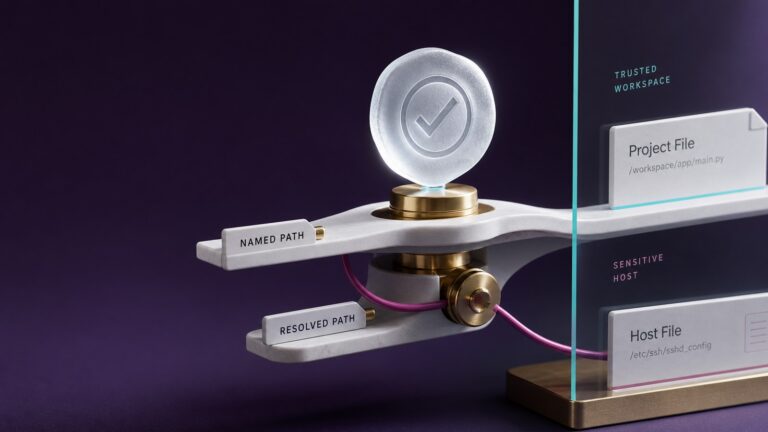
Many hybrid apps fail because navigation rules are too broad. A WebView starts on an allowed domain, then follows redirects, opens deep links, loads iframes, processes universal links, or accepts server-driven content that introduces a weaker origin. A review should inspect shouldOverrideUrlLoading, shouldInterceptRequest, custom scheme handling, redirect handling, and whether the app validates scheme, host, path, and expected state.
Allowlisting must be exact. endsWith() host checks, substring matching, accepting arbitrary HTTPS URLs, or treating a marketing domain as equivalent to an authenticated application domain are all recurring mistakes.
File access and local content
File access settings can turn local HTML into a data-exfiltration primitive. If local content can run JavaScript and read other local files, a small injection or navigation bug becomes more serious. Review allowFileAccess, allowContentAccess, allowFileAccessFromFileURLs, and allowUniversalAccessFromFileURLs. The safe baseline is to disable what is not required and separate trusted local assets from remote or user-controlled content.
Also test how WebView interacts with cache, cookies, local storage, IndexedDB, downloads, clipboard, screenshots, and exported file providers. Sensitive data often survives longer in web storage than teams expect.
Deep links into WebView
Deep links are a common way to turn WebView from a rendering detail into an attack surface. If an external intent can choose the URL, path, fragment, query string, post-login route, or JavaScript-relevant state, the WebView becomes reachable from outside the app.
The most interesting bugs appear when a deep link lands the victim inside an already authenticated WebView session. From there, open redirects, weak origin checks, injected parameters, or bridge exposure may convert a link click into account action, token leakage, or native capability abuse.
Better patterns
For modern Android apps, prefer custom tabs or external browsers when the content does not need native trust. If a WebView is required, keep JavaScript disabled unless necessary, avoid native bridges unless the content is fully controlled, use AndroidX WebKit APIs with feature checks, constrain message listeners with origin rules, and validate messages as an API contract rather than as loose strings from “our frontend.”
The secure design pattern is boring but effective: one WebView purpose, one trust level, exact origin allowlists, minimal native capability, strict navigation policy, no arbitrary deep-linked URLs, and server-side authorization for every sensitive action.
Assessment checklist
A useful WebView review should answer: What content can load? Who controls that content? Which origins can access native bridges? Can external intents influence the URL? Are file and content access settings needed? Does the app mix authenticated session state with untrusted navigation? Are redirects constrained? Can injected JavaScript reach native methods? Are cookies scoped and cleared correctly on logout? Is sensitive state duplicated between native and web storage?
If these questions are not answered explicitly in the design, WebView will continue to be a mess.
References
💜 Enjoyed this content? Support the blog with USDT (TRC20):
TX7obcjHQbDUXb4mGqoASEu1QFTKT2CFGG