GhostApproval: When AI Agent Approval Dialogs Lie
GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.

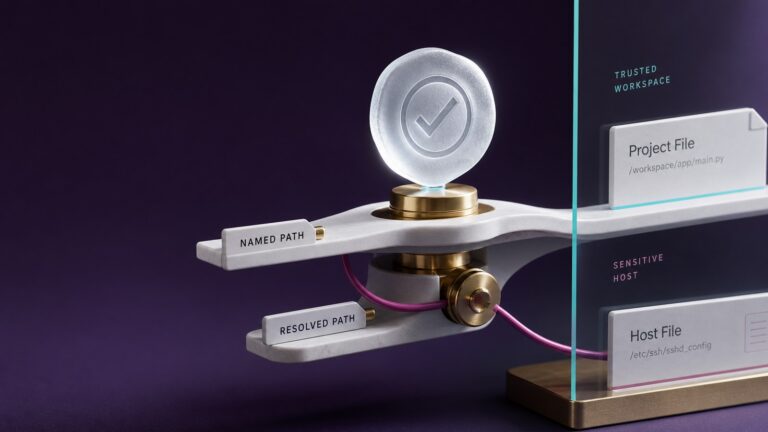
GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.
WebView remains one of the most productive Android AppSec targets because hybrid apps repeatedly mix trusted native capabilities with untrusted or weakly controlled web content.
Android mobile app security is rarely broken by a single missing root check. The higher-impact failures are usually architectural: trusting the client, storing secrets on the device, exposing components, and assuming Frida detection or emulator checks can compensate for weak server-side controls.
The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.
A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
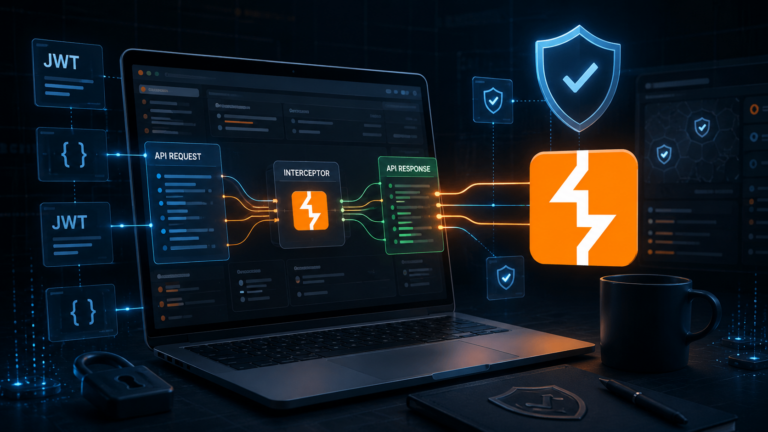
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
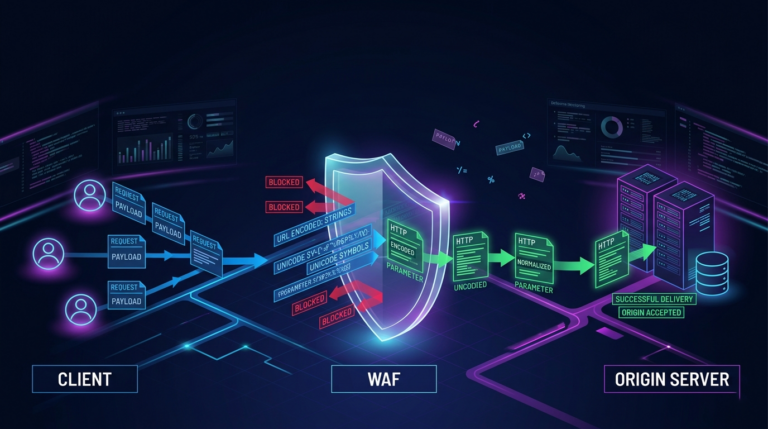
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
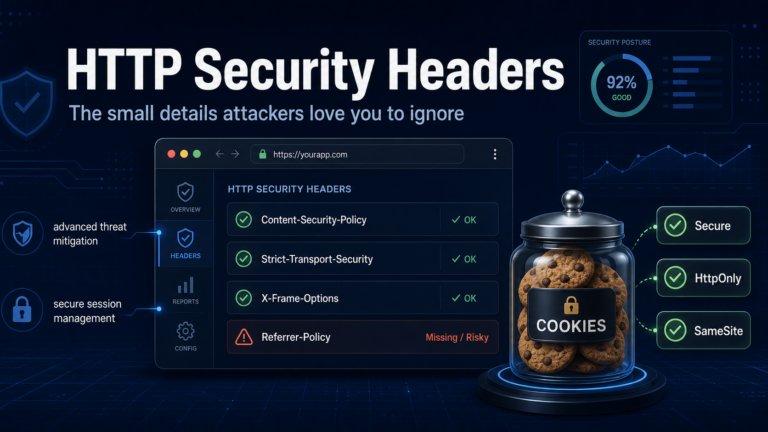
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.