The Proxy Saw One Request: http4s Ember HTTP Desync
Three http4s Ember flaws let proxies and origins disagree about HTTP request boundaries. Trace the mechanics, safe lab, detection, and durable fixes.

Three http4s Ember flaws let proxies and origins disagree about HTTP request boundaries. Trace the mechanics, safe lab, detection, and durable fixes.
Jenkins configuration forms can become constructor dispatch. Trace the September 2026 flaws, a safe mechanism lab, detection signals, and durable fixes.
CVE-2026-47849 let JSON Patch mutate Spring Data REST identifiers and version fields. This analysis verifies the binding flaw, traces the cross-record overwrite path, and maps practical detection and hardening controls.
CVE-2026-60004 turns duplicate Gitea diffpatch requests into an executable Git hook. Analyze the attack chain, detection signals, and containment.
CVE-2026-61539 turned attacker-influenced Llama tool output into Python RCE inside Xinference. This analysis traces the parser boundary, validates the primitive in a safe local lab, and maps durable detection and hardening controls.
CVE-2026-63077 exposes every TeamCity On-Premises version to unauthenticated RCE through the agent polling protocol. This deep dive maps the trust failure, runs a safe deserialization mechanism lab, and shows how to detect, contain, and validate CI/CD integrity.
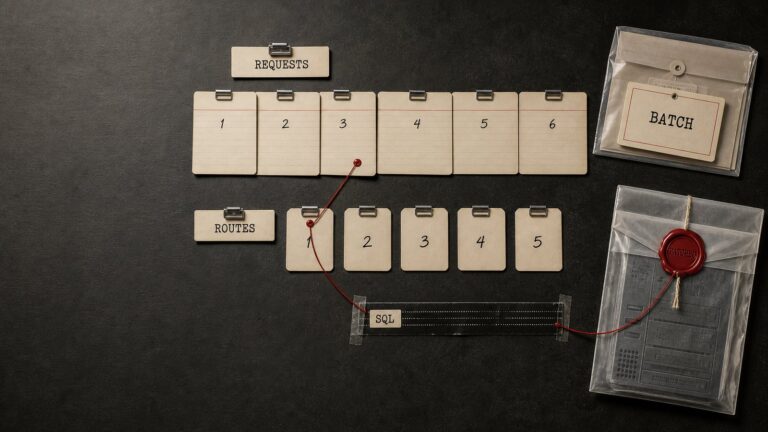
wp2shell chains WordPress REST route confusion with SQL injection to reach pre-auth RCE. Learn the mechanics, affected versions, evidence sources, and safe response workflow.
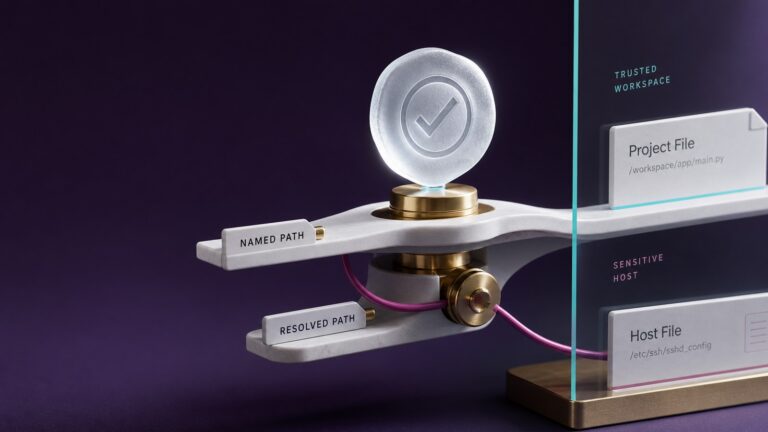
GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.
WebView remains one of the most productive Android AppSec targets because hybrid apps repeatedly mix trusted native capabilities with untrusted or weakly controlled web content.
Android mobile app security is rarely broken by a single missing root check. The higher-impact failures are usually architectural: trusting the client, storing secrets on the device, exposing components, and assuming Frida detection or emulator checks can compensate for weak server-side controls.
The five vulnerability classes that most often command the highest bug bounty payouts, with advanced local-lab examples, impact validation, mitigation guidance, and tips for stronger reports.
A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
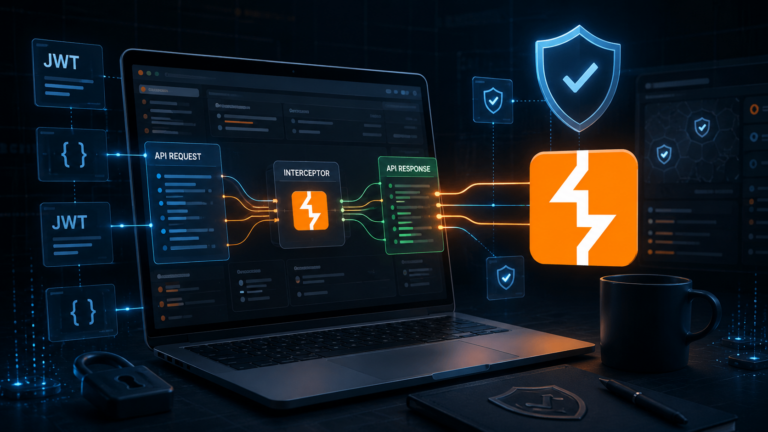
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
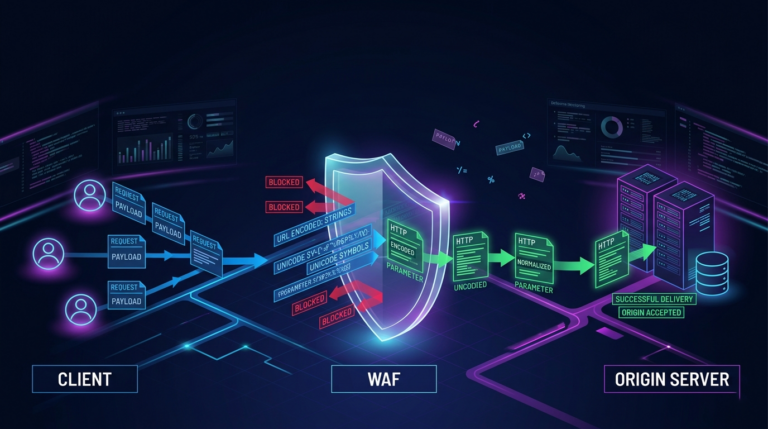
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
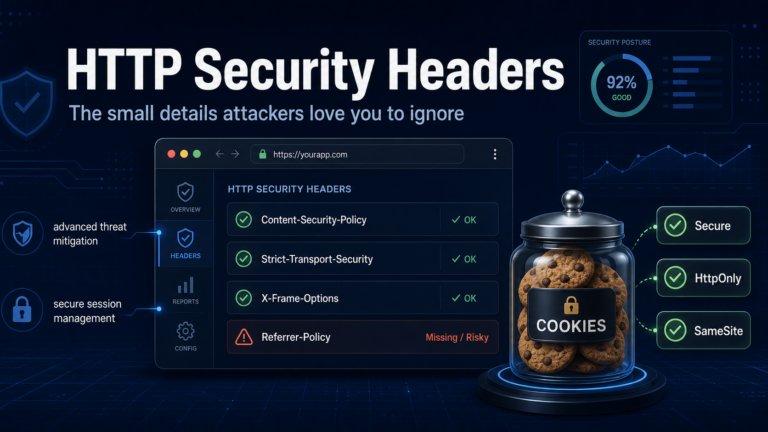
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.







