The Shard Had Two Identities: Elasticsearch CVE-2026-103009
CVE-2026-103009 let cross-cluster authorization validate one shard identity while execution followed another. Trace the patch, detection, and hardening.

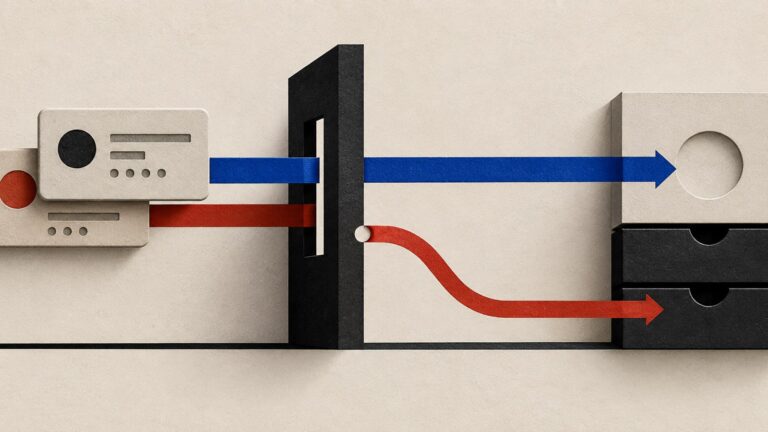
CVE-2026-103009 let cross-cluster authorization validate one shard identity while execution followed another. Trace the patch, detection, and hardening.
CVE-2026-47849 let JSON Patch mutate Spring Data REST identifiers and version fields. This analysis verifies the binding flaw, traces the cross-record overwrite path, and maps practical detection and hardening controls.
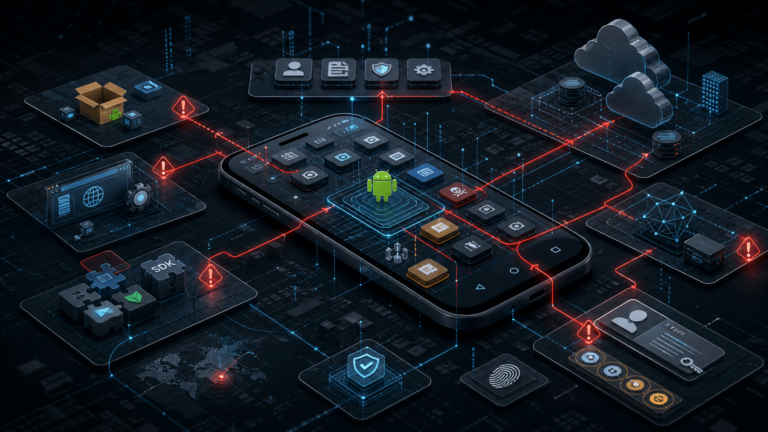
Android security research still pays off, but the best bugs now sit across APK logic, identity flows, backend APIs, SDK trust boundaries, WebView surfaces, and abuse-resistant controls such as attestation.
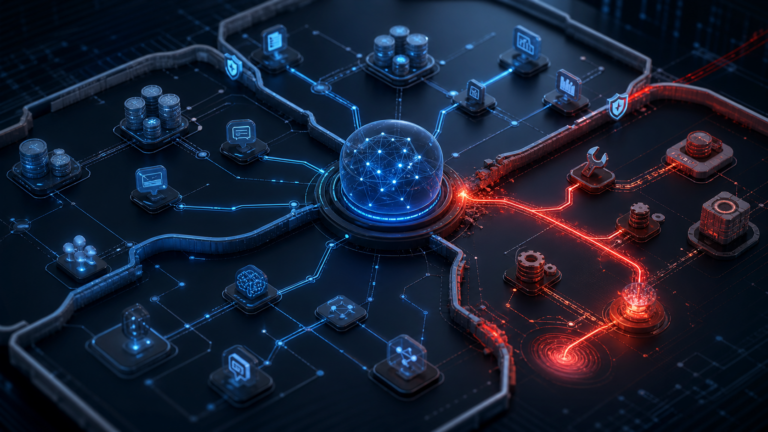
Technical analysis of enterprise AI attack chains: indirect prompt injection, memory poisoning, tool abuse, MCP exposure, and detection.
Advanced guide to AI threat modeling for RAG, agents, and MCP, with trust boundaries, context provenance, and identity separation.
A practical AI Red Team guide to A2A reconnaissance, canary agent registration, agent-card spoofing, and delegation auditing in an authorized lab.
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.
An advanced guide to defensive corporate OSINT from a Red Team perspective, covering identity, cloud, APIs, detection, and real attack chains.
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
A practical lab-based methodology for assessing router security with Claude, MCP, controlled recon, vendor disclosure, and defensible evidence handling.