HackerDNA: 4 Steps to Train for Pentesting
How to use ethical hacking labs to train enumeration, exploitation, evidence gathering, and reporting discipline without falling into CTF habits.

How to use ethical hacking labs to train enumeration, exploitation, evidence gathering, and reporting discipline without falling into CTF habits.
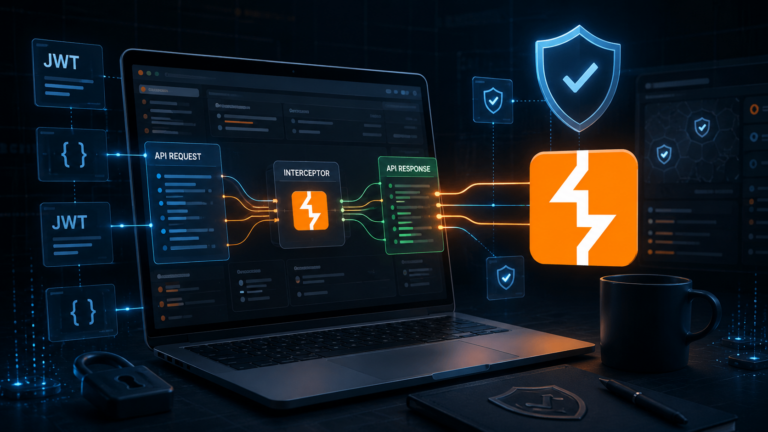
An AppSec guide to building safe Burp Suite extensions for authorized API assessments across JWT, BOLA/IDOR, mass assignment, rate limiting, OpenAPI drift, and evidence collection.
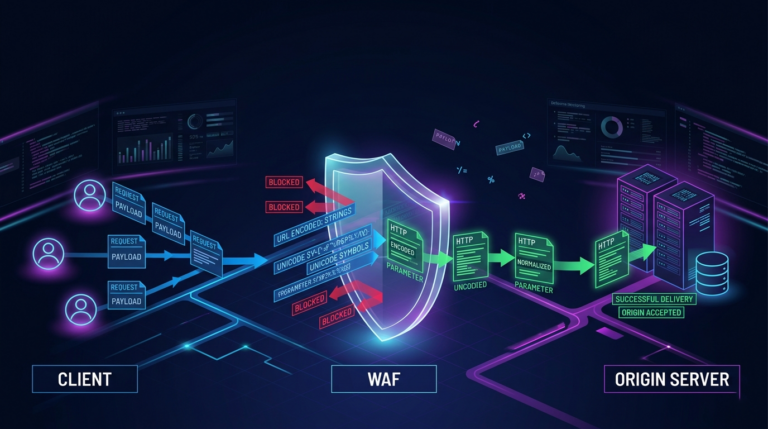
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
Prompt injection is not theoretical. It is a real vulnerability affecting AI applications through direct, indirect, multimodal, and RAG-based attack paths. This guide covers vectors, POCs, evasion techniques, testing, and defenses.
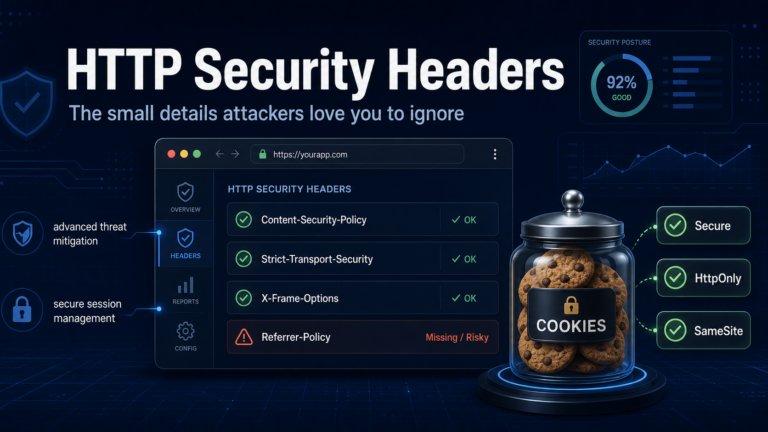
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.
Why running Nmap on Android changes internal recon: faster enumeration from a mobile foothold, realistic constraints, and practical offensive tradecraft.







