MCP Security: How to Secure Agents, Tools, and Servers
MCP security in practice: the main Model Context Protocol risks, from indirect prompt injection to excessive privileges, and a practical hardening framework for agents, clients, and servers.

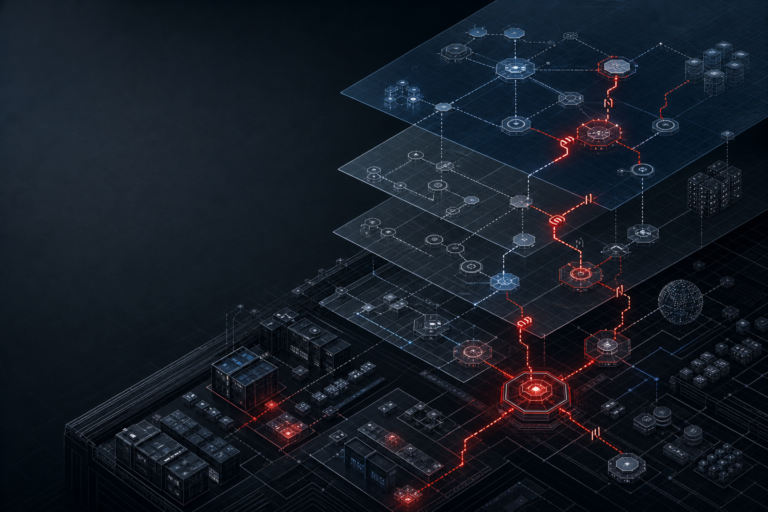
MCP security in practice: the main Model Context Protocol risks, from indirect prompt injection to excessive privileges, and a practical hardening framework for agents, clients, and servers.
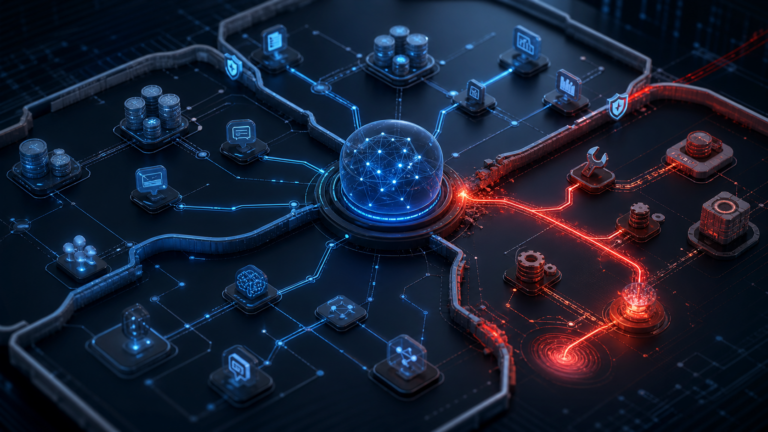
Technical analysis of enterprise AI attack chains: indirect prompt injection, memory poisoning, tool abuse, MCP exposure, and detection.
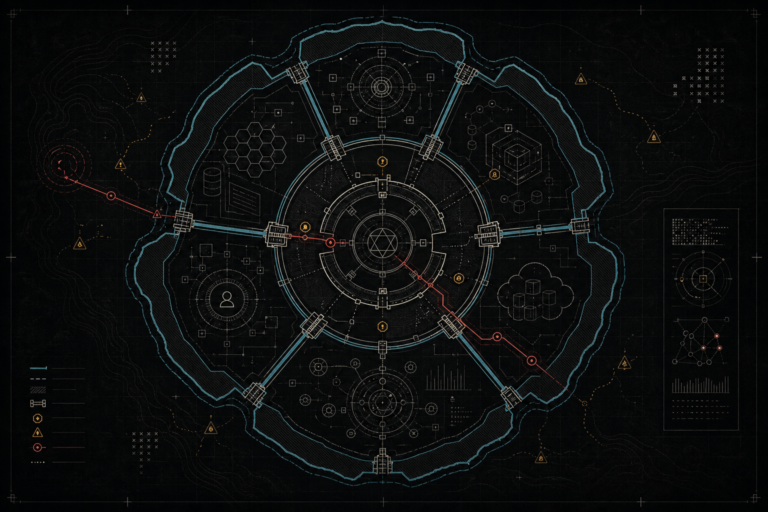
Advanced guide to AI threat modeling for RAG, agents, and MCP, with trust boundaries, context provenance, and identity separation.
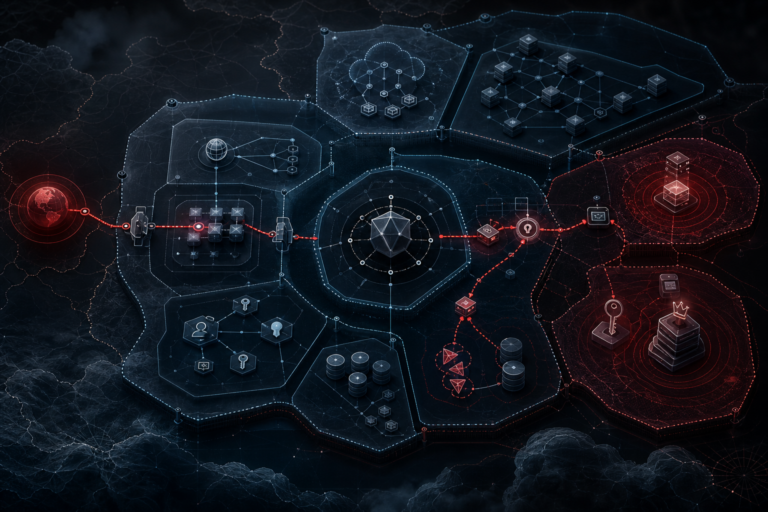
Advanced threat modeling in practice: identities, trust boundaries, SSRF, cloud metadata, delegated tokens, and blast radius across real attack chains.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.







