Android App Security: Root Detection, Frida, and the Failure of Client-Side Trust
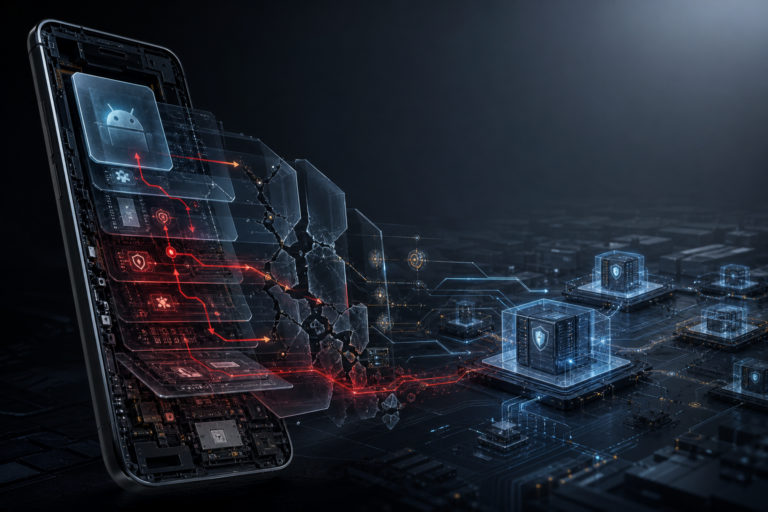
Android mobile app security is rarely broken by a single missing root check. The higher-impact failures are usually architectural: trusting the client, storing secrets on the device, exposing components, and assuming Frida detection or emulator checks can compensate for weak server-side controls.