The Approval Bound the Wrong Commit: GitHub Actions TOCTOU
A privileged workflow can inherit secrets, write tokens, and attacker-controlled artifacts. Learn how to bind the GitHub Actions handoff to immutable evidence.

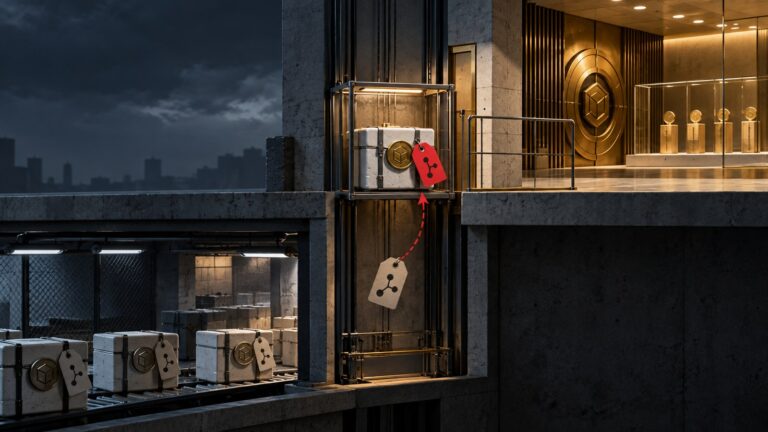
A privileged workflow can inherit secrets, write tokens, and attacker-controlled artifacts. Learn how to bind the GitHub Actions handoff to immutable evidence.
CVE-2026-97229 lets a crafted CI regular expression reach GitLab native compilation and potentially execute code on the server. Trace the integer-wrap mechanics, patch evolution, safe lab, detection, and control-plane response.
CVE-2026-102870 lets attacker-controlled Blazor application data escape into generated debugger source. This analysis maps the developer-workstation attack chain, a safe mechanism lab, patch scope, and detection opportunities.
Five Nuclei flaws show how alternate loaders, embedded runtimes, and response evaluation can turn a security scanner into the asset under attack.
Jenkins configuration forms can become constructor dispatch. Trace the September 2026 flaws, a safe mechanism lab, detection signals, and durable fixes.
CVE-2026-60004 turns duplicate Gitea diffpatch requests into an executable Git hook. Analyze the attack chain, detection signals, and containment.
CISA’s 2026 SBOM baseline improves software identity and evidence quality. This advanced guide turns that inventory into an auditable VEX pipeline for exploitability decisions, release policy, and detection.
CVE-2026-63077 exposes every TeamCity On-Premises version to unauthenticated RCE through the agent polling protocol. This deep dive maps the trust failure, runs a safe deserialization mechanism lab, and shows how to detect, contain, and validate CI/CD integrity.
GitLost turned a public GitHub issue into a private-repository disclosure. Trace the confused-deputy chain, reproduce it safely, and harden agentic CI.
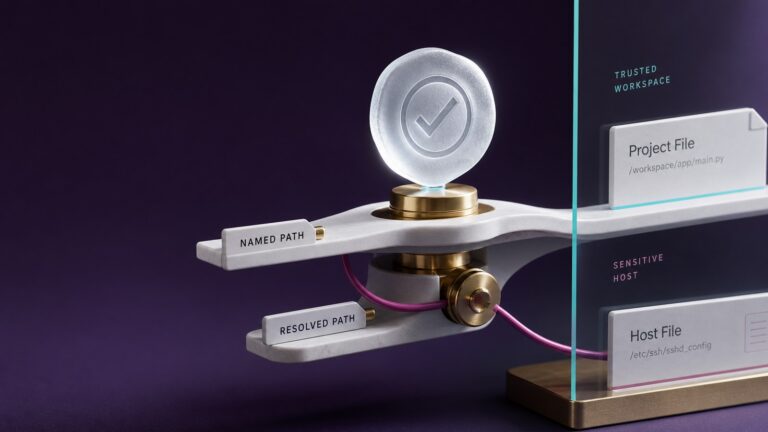
GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.
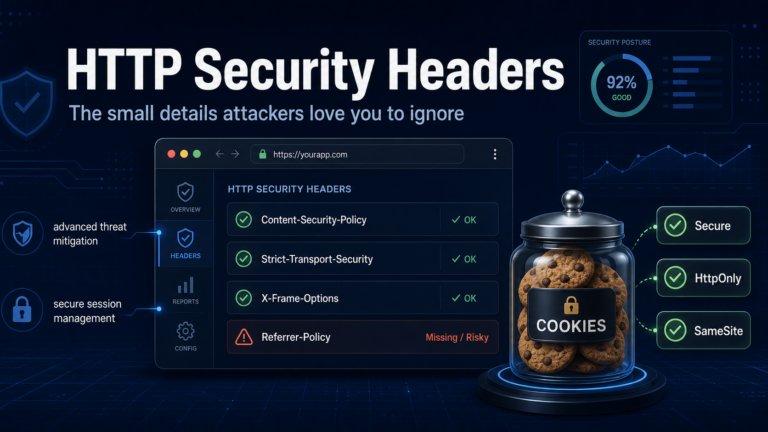
Attackers love neglected basics. This post shows how HTTP security headers and cookie flags such as HttpOnly, Secure, and SameSite shape real defensive posture.