MCP Security: Tools and Permissions in Practice
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.

MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
OpenSSH 10.3 addresses risks in the SSH client, certificates, forwarding, and legacy scp. Here is the impact, a Blue Team checklist, and safe defensive PoCs.
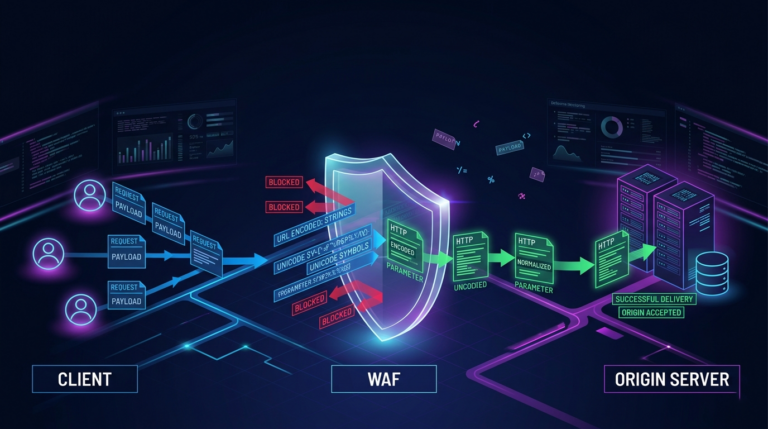
Learn real WAF bypass techniques, how to validate evidence safely, and which controls to apply for detection and mitigation in defensive environments.
AI as C2 is a real threat in enterprise environments. This guide covers 5 critical risks, detection indicators, and practical defenses for Blue Team.







