GitLost: When a Public Issue Can Read a Private Repo
GitLost turned a public GitHub issue into a private-repository disclosure. Trace the confused-deputy chain, reproduce it safely, and harden agentic CI.

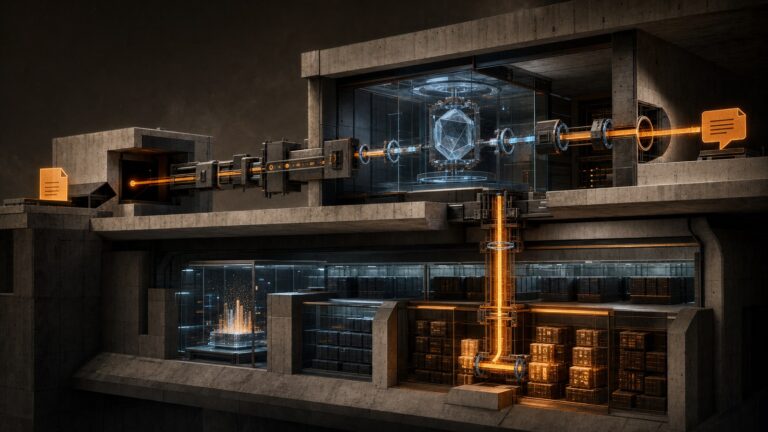
GitLost turned a public GitHub issue into a private-repository disclosure. Trace the confused-deputy chain, reproduce it safely, and harden agentic CI.
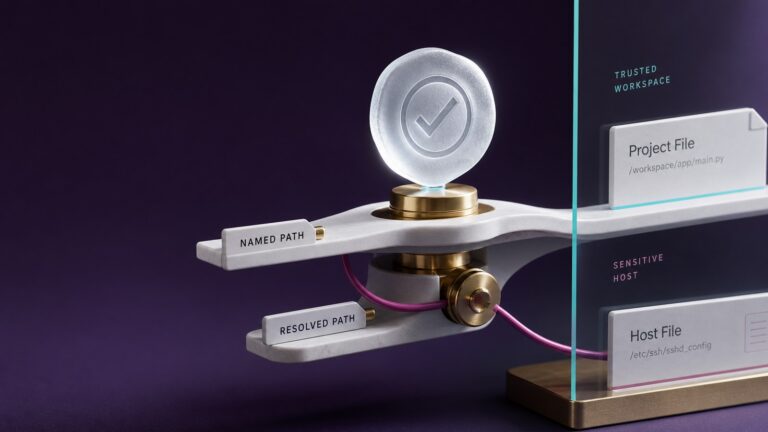
GhostApproval turns a harmless-looking AI agent edit into an out-of-workspace write. Learn the symlink mechanics, safe lab reproduction, detection, and race-resistant defenses.
MCP security in practice: the main Model Context Protocol risks, from indirect prompt injection to excessive privileges, and a practical hardening framework for agents, clients, and servers.
A practical AI Red Team guide to A2A reconnaissance, canary agent registration, agent-card spoofing, and delegation auditing in an authorized lab.
MCP Security in practice: a safe lab with fictional documents, a mocked local agent, controlled tool exploitation, permissions, schemas, and auditable logs.
A practical AI Red Team guide for testing agents, RAG, memory, tools, and autonomy workflows beyond prompt injection, with checklists, metrics, and controls.
Authorized reconnaissance for enterprise AI: map LLMs, RAG pipelines, agents, tools, IAM, APIs, cloud exposure, and evidence without drifting out of scope.
Autonomous Pentest Agents can accelerate Red Team operations, but they also introduce risk around prompt injection, tool misuse, scope control, evidence quality, and detection.







